Product tour
CISO Assistant, screen by screen
Real screens from a demo instance, from the analytics dashboard to the API.
Analytics
Your whole program on one screen
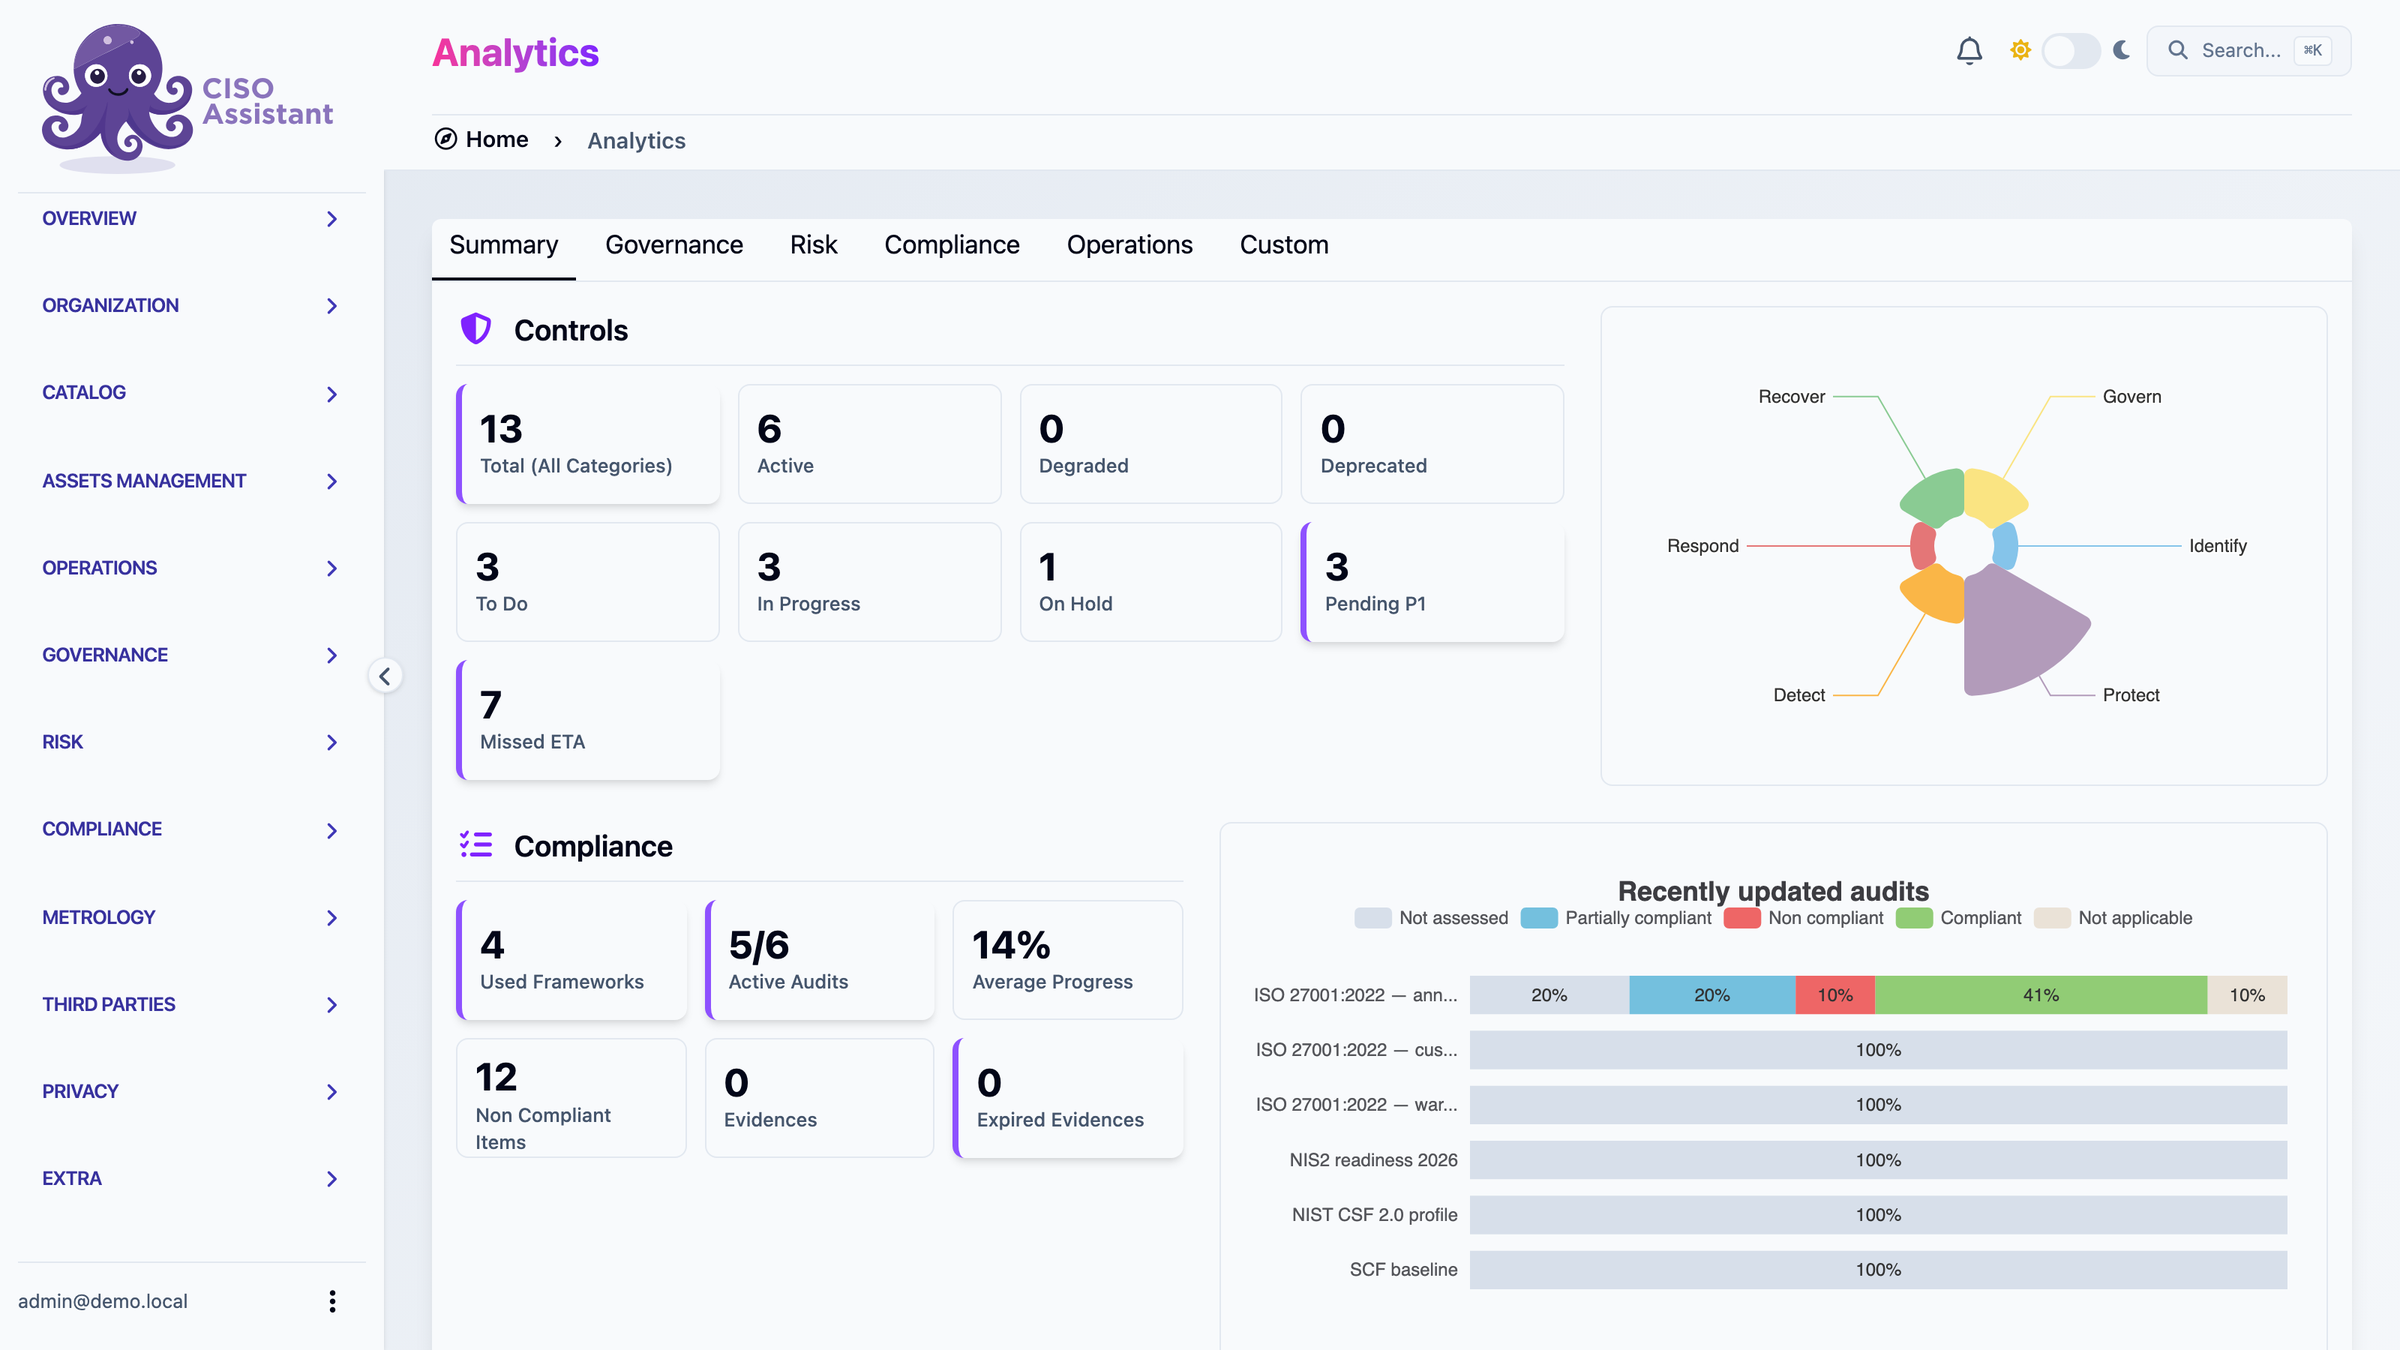
Controls by status, compliance across active audits and the progress of every audit.
Library
Start from a library, not a blank page
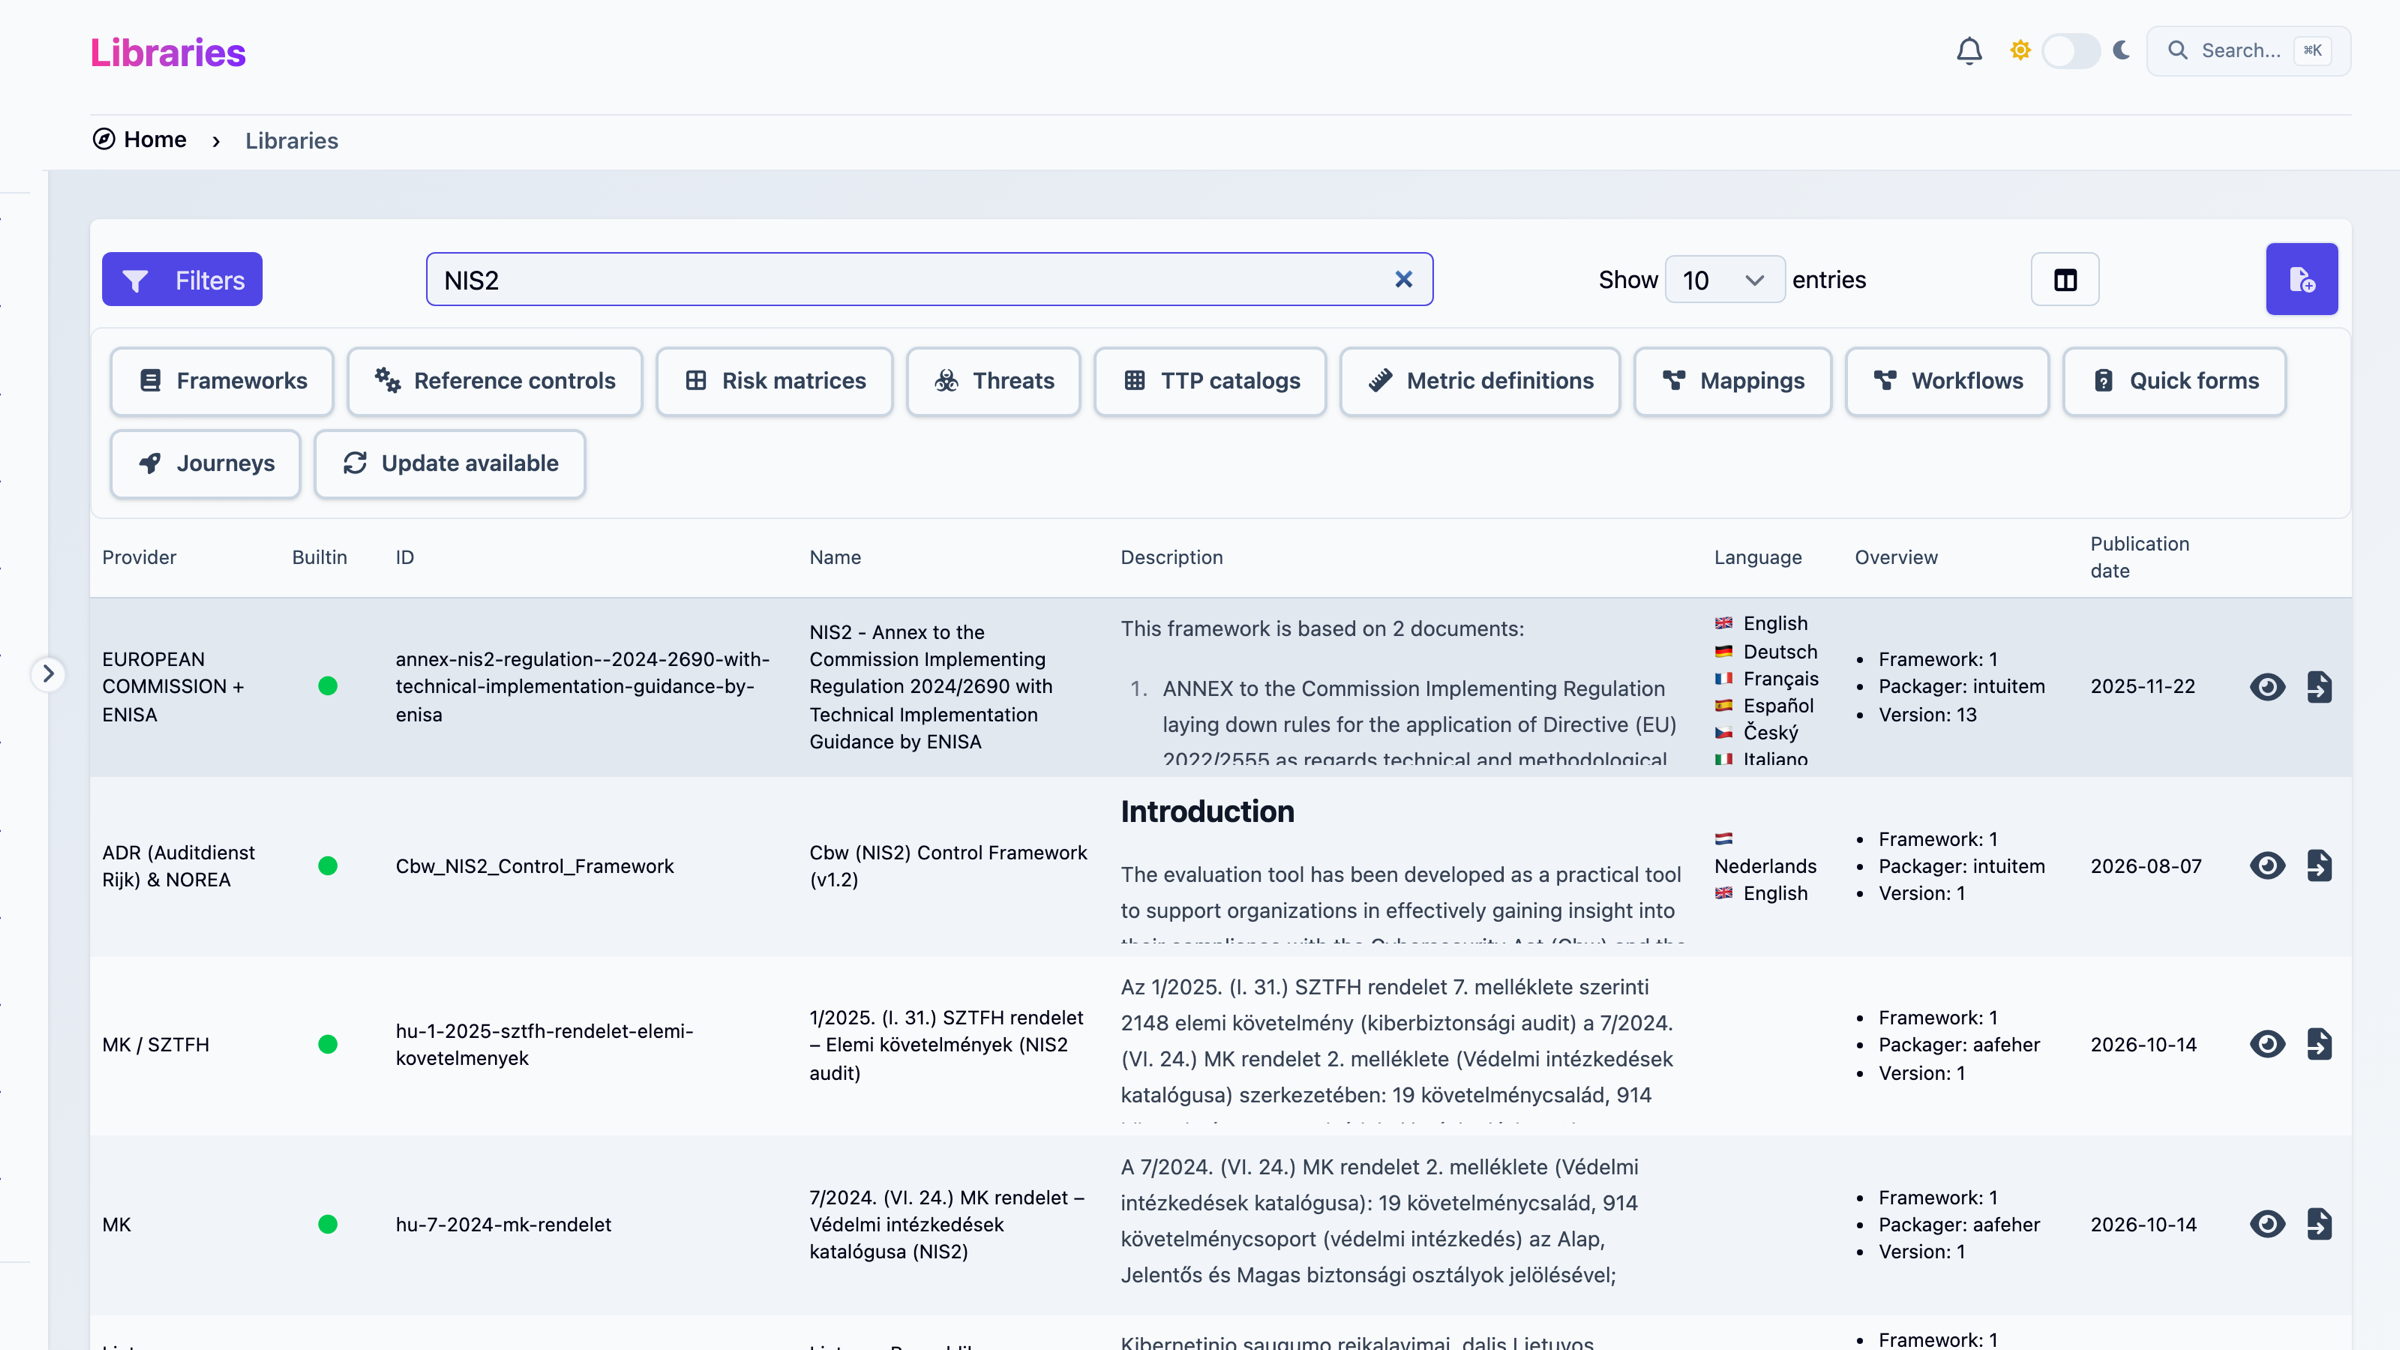
More than 200 frameworks, from NIS2 and its national transpositions to ISO and NIST, plus mappings, risk matrices, threat catalogs, reference controls and workflows, loaded in one click.
Library builder
Write your own frameworks and forms
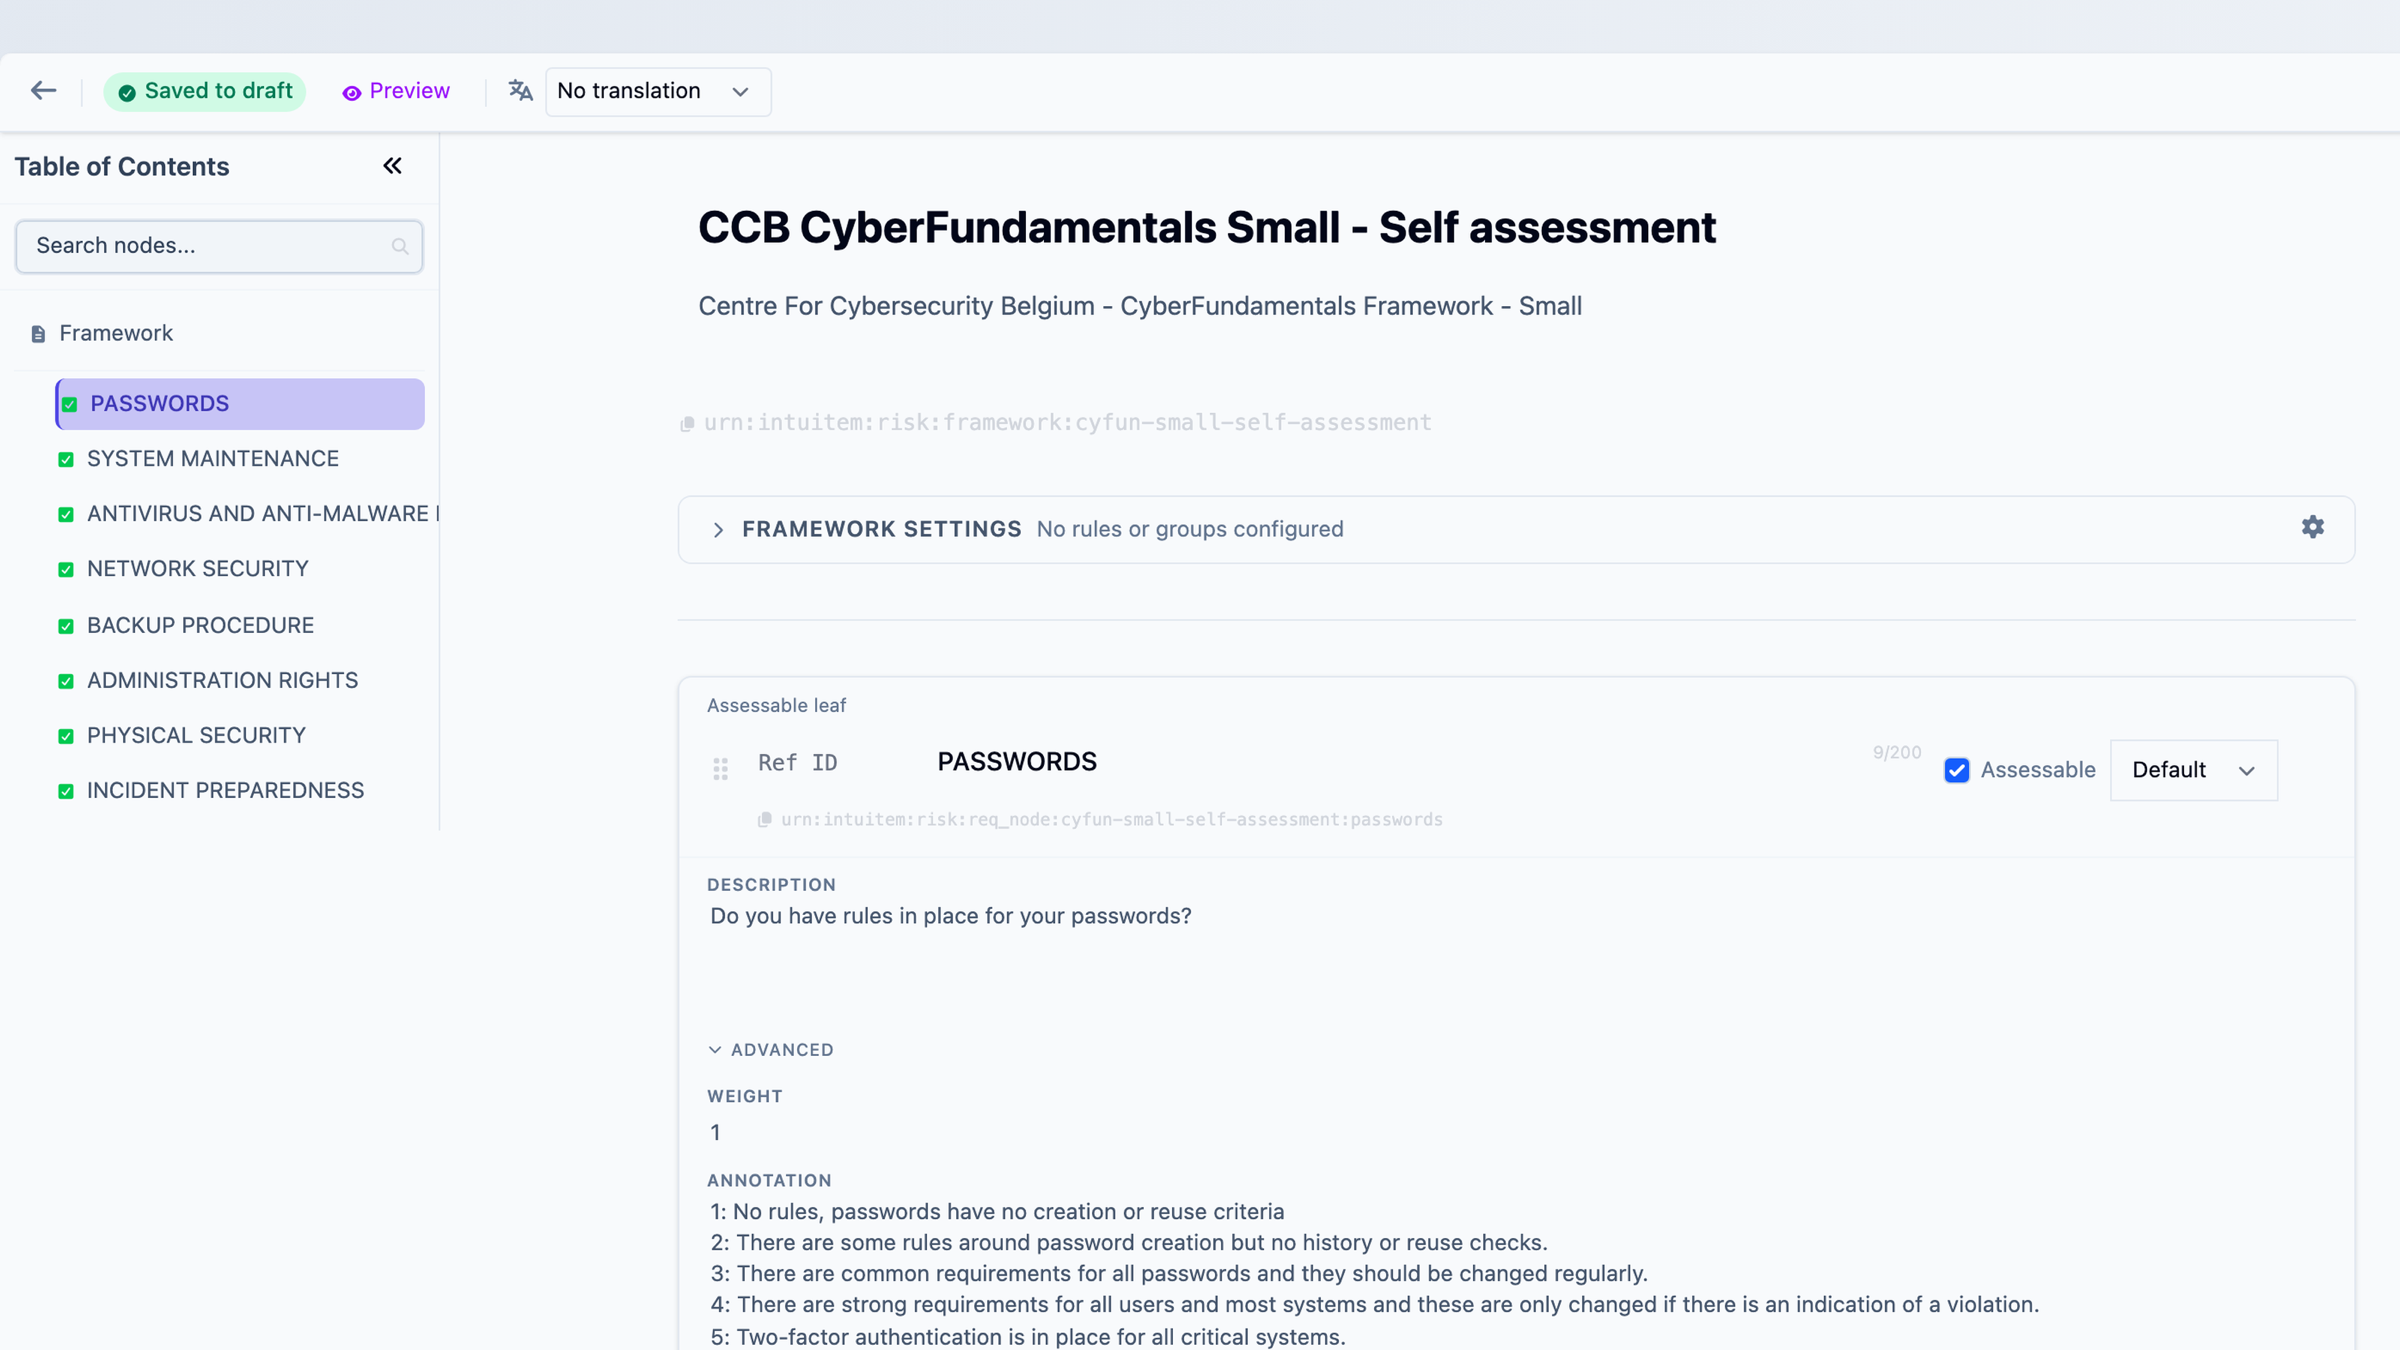
Author a framework, a risk matrix or a quick form in a visual editor, or import an existing one and adapt it, then publish it like any library in the catalog.
Audits
An ISO 27001 audit from start to finish
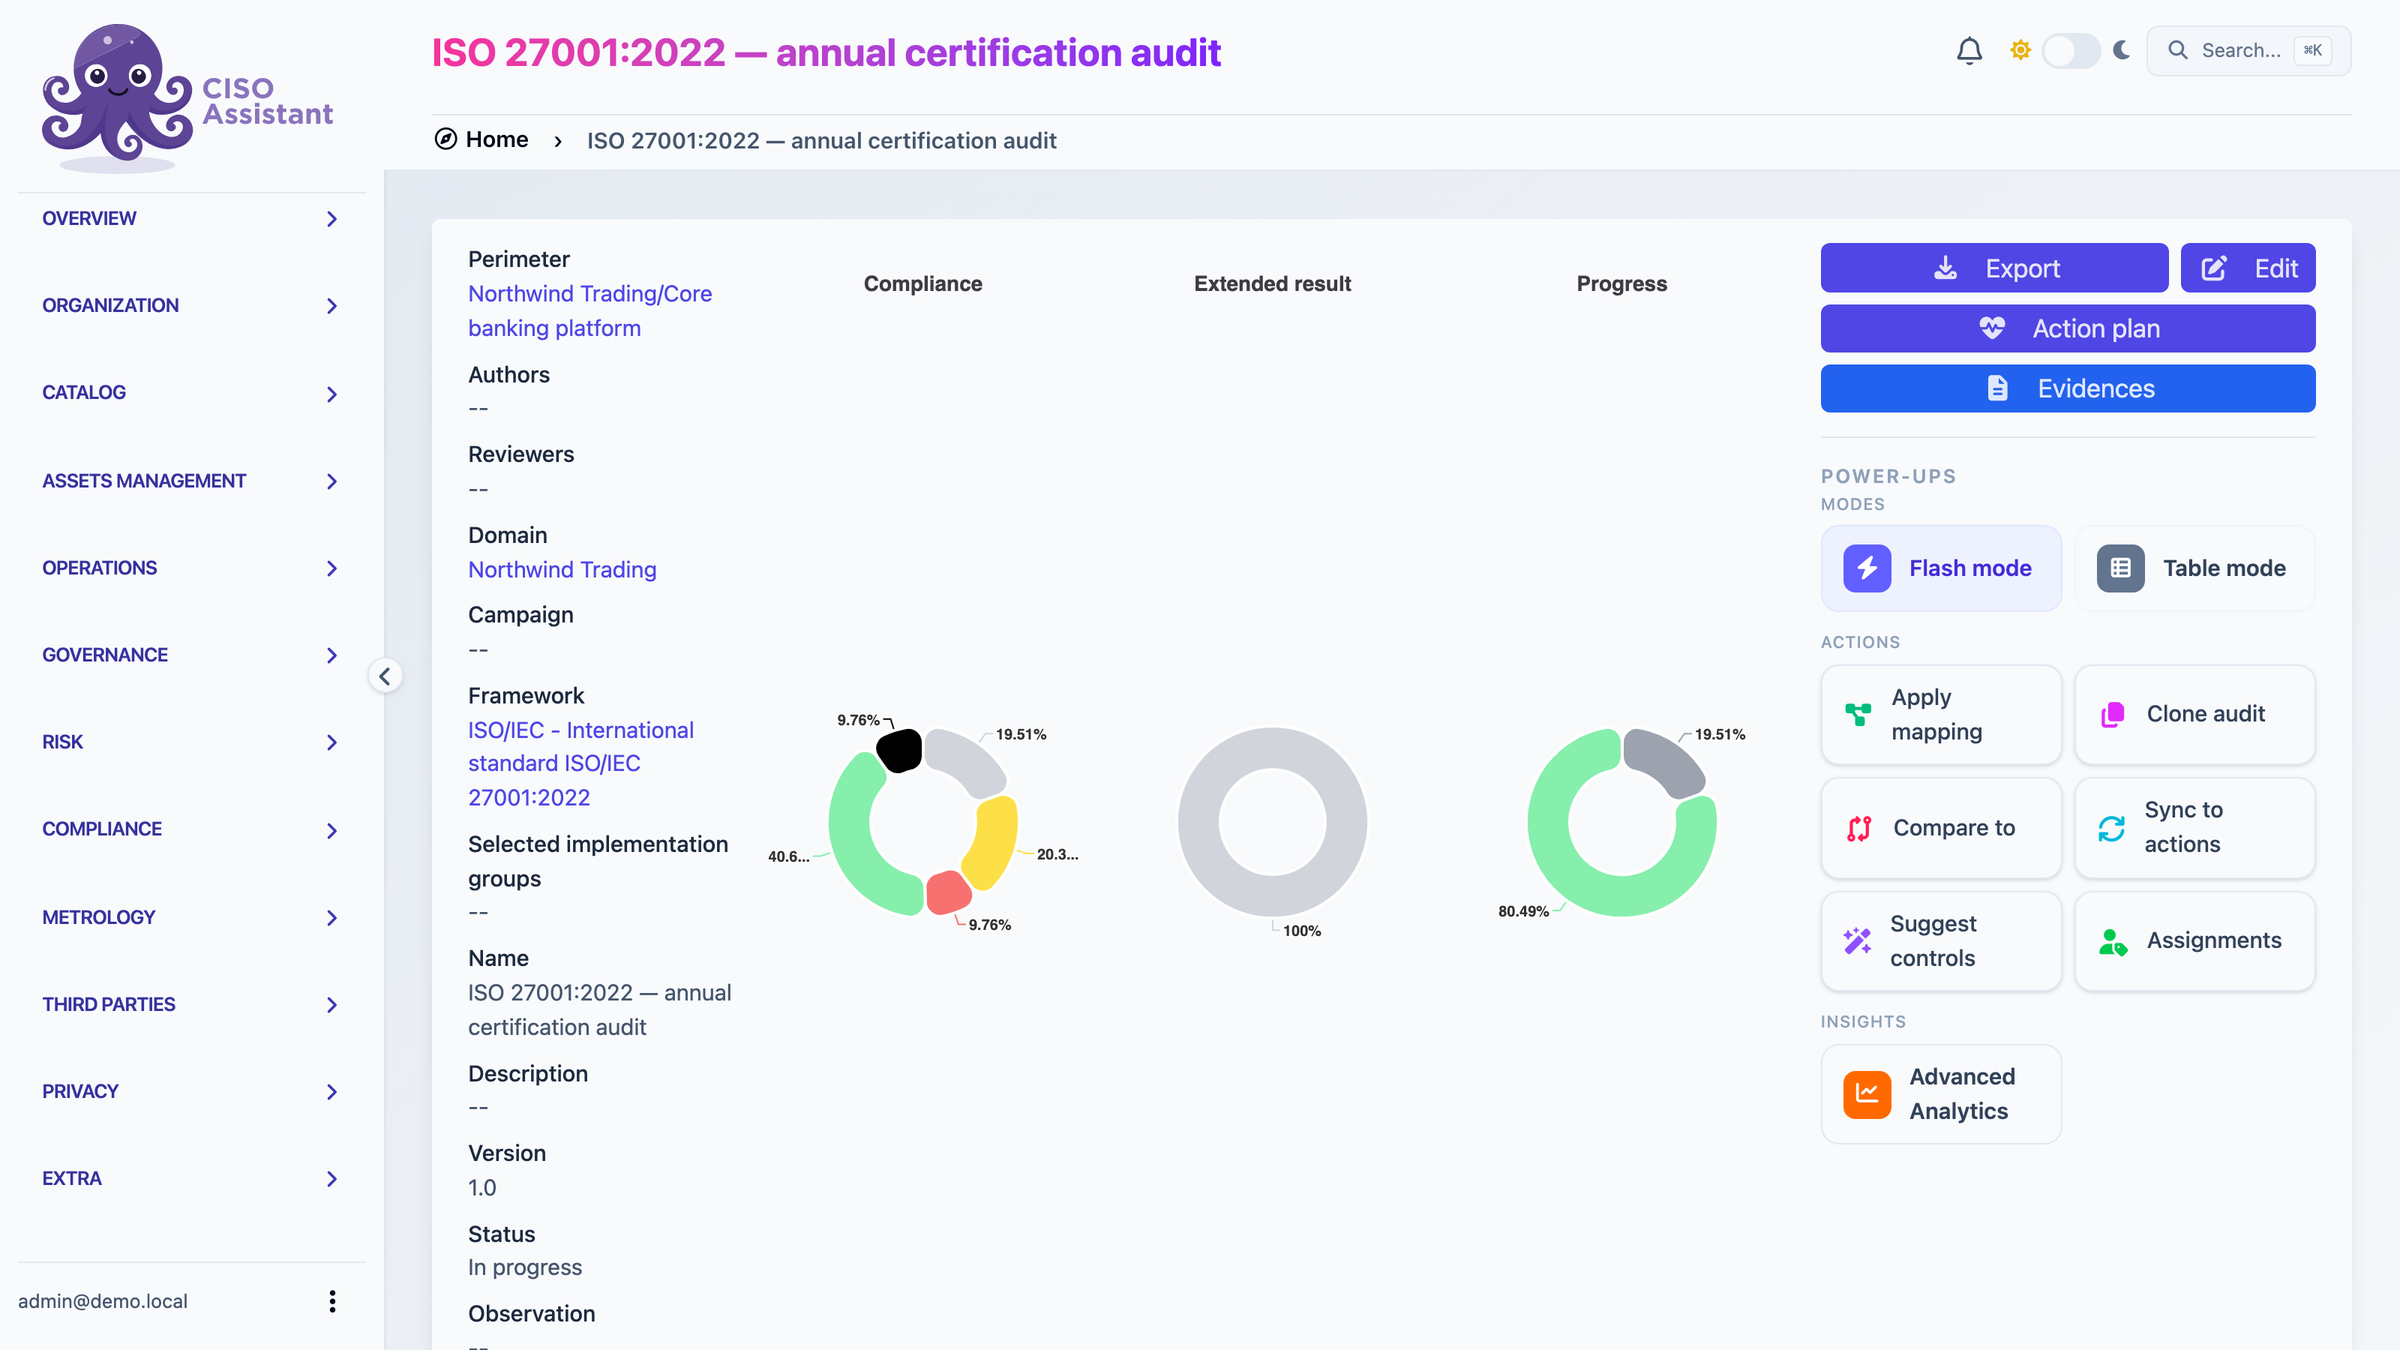
Compliance and progress at a glance, flash mode and table mode for fast assessment, and the action plan and evidence one click away.
Mappings
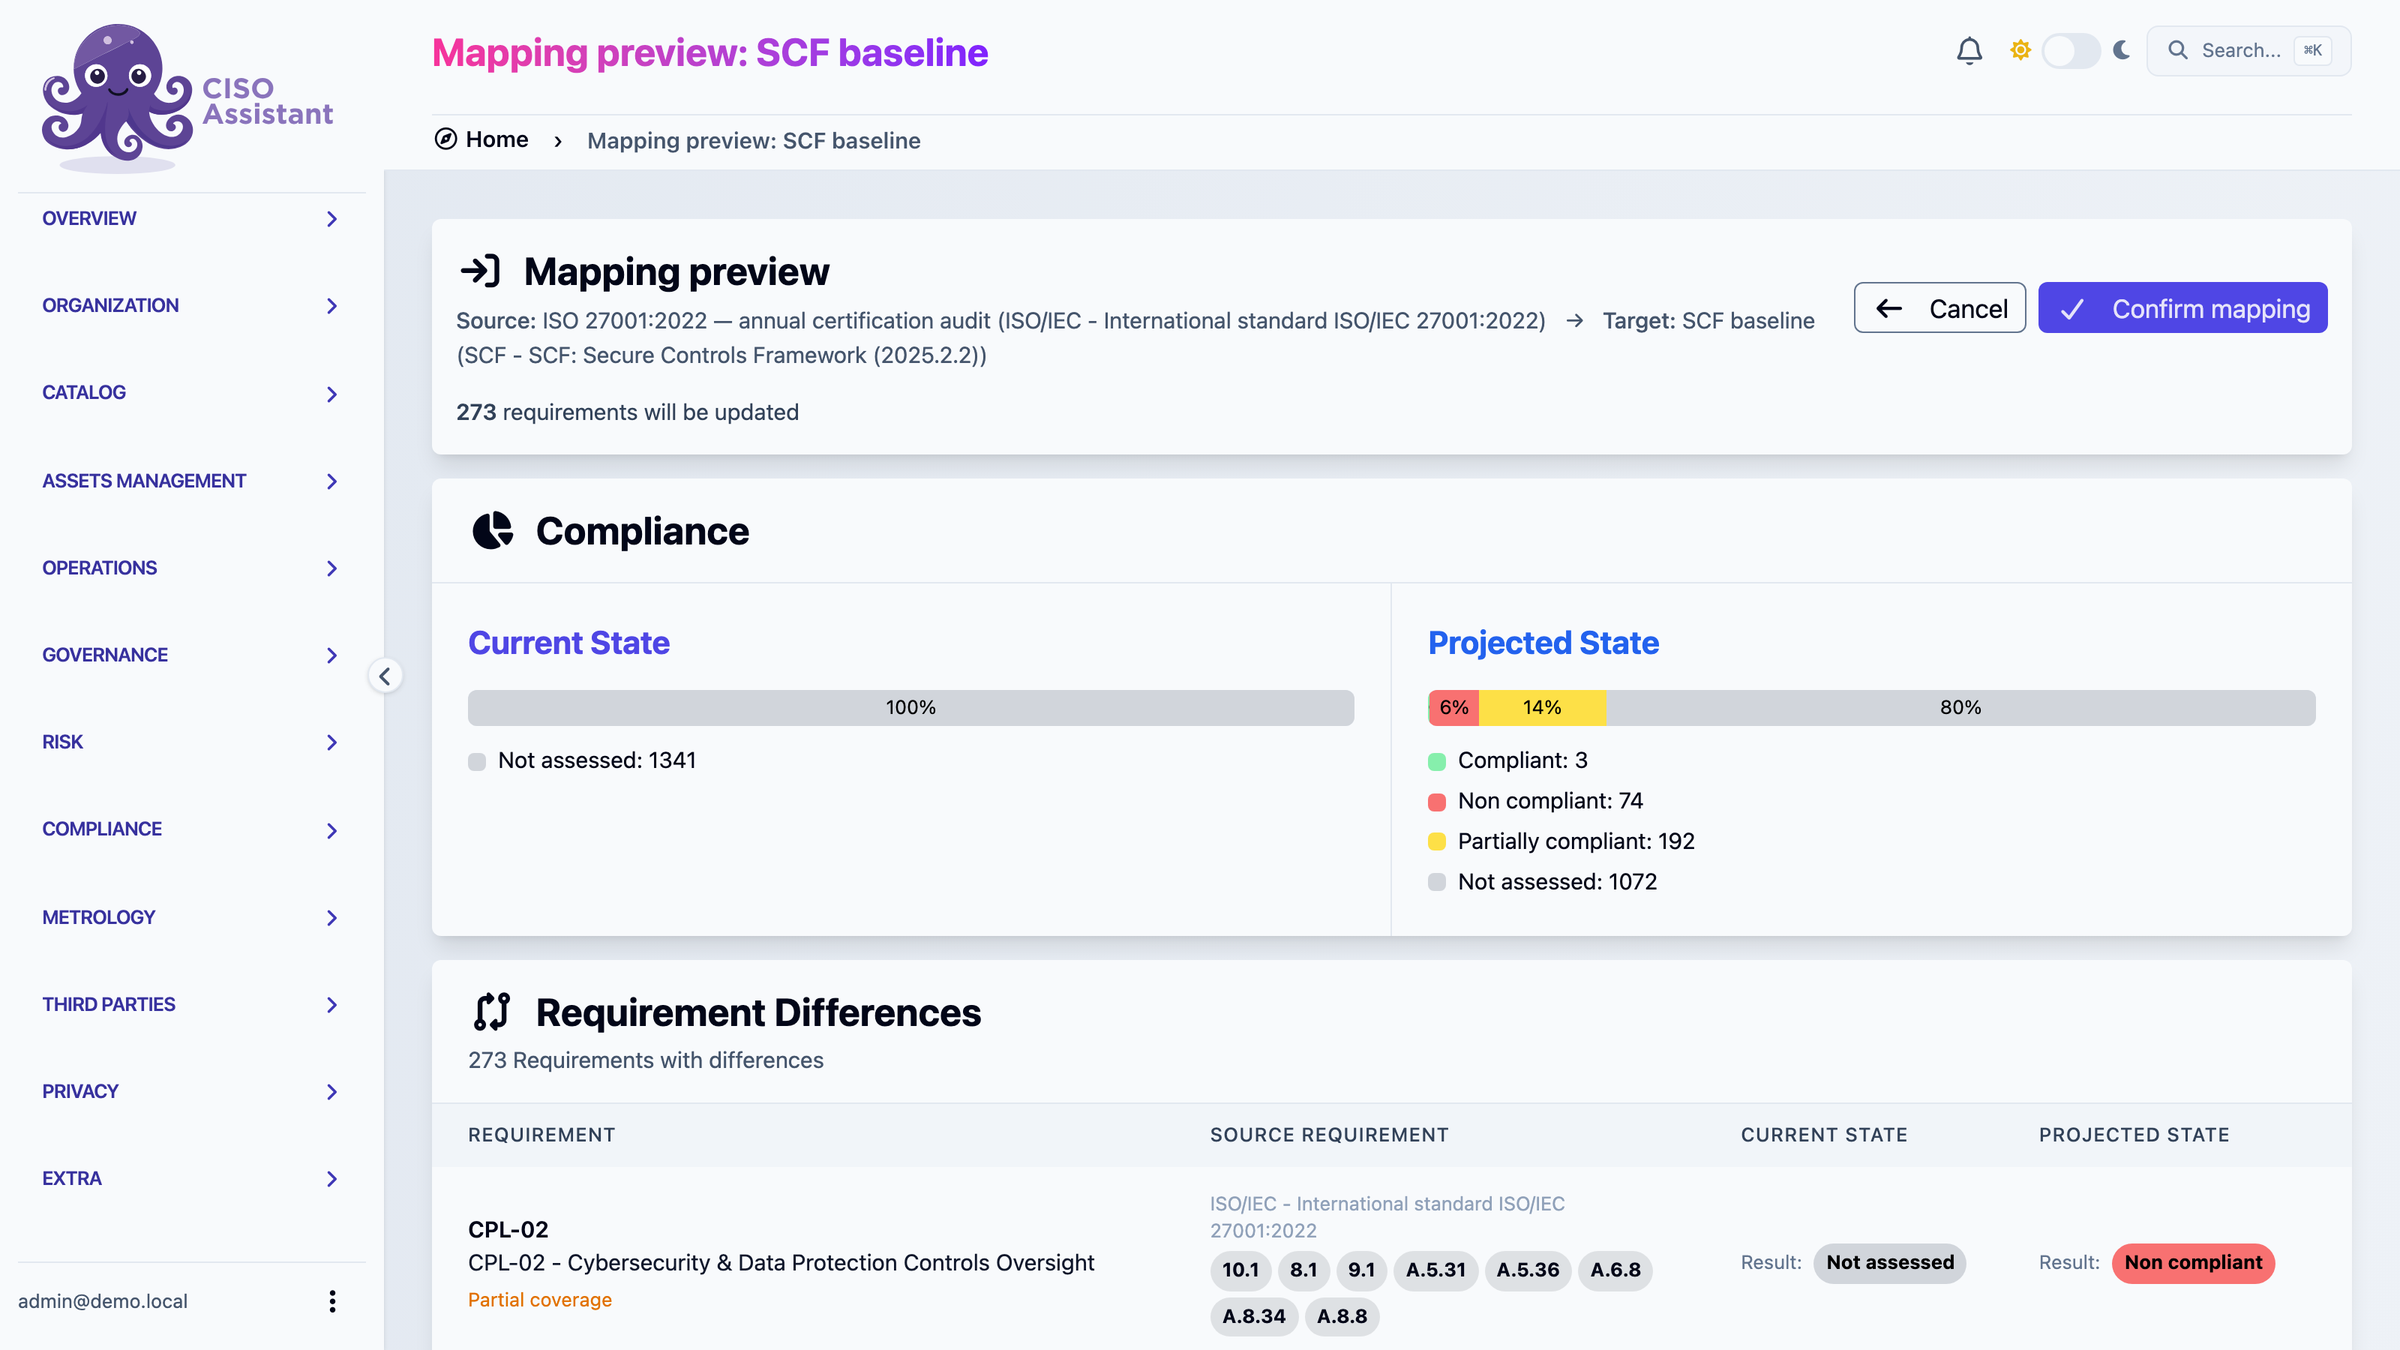
Reuse an audit on another framework
Map an ISO 27001 audit onto the SCF baseline: preview the projected compliance and every changed requirement before you confirm.
Control reuse
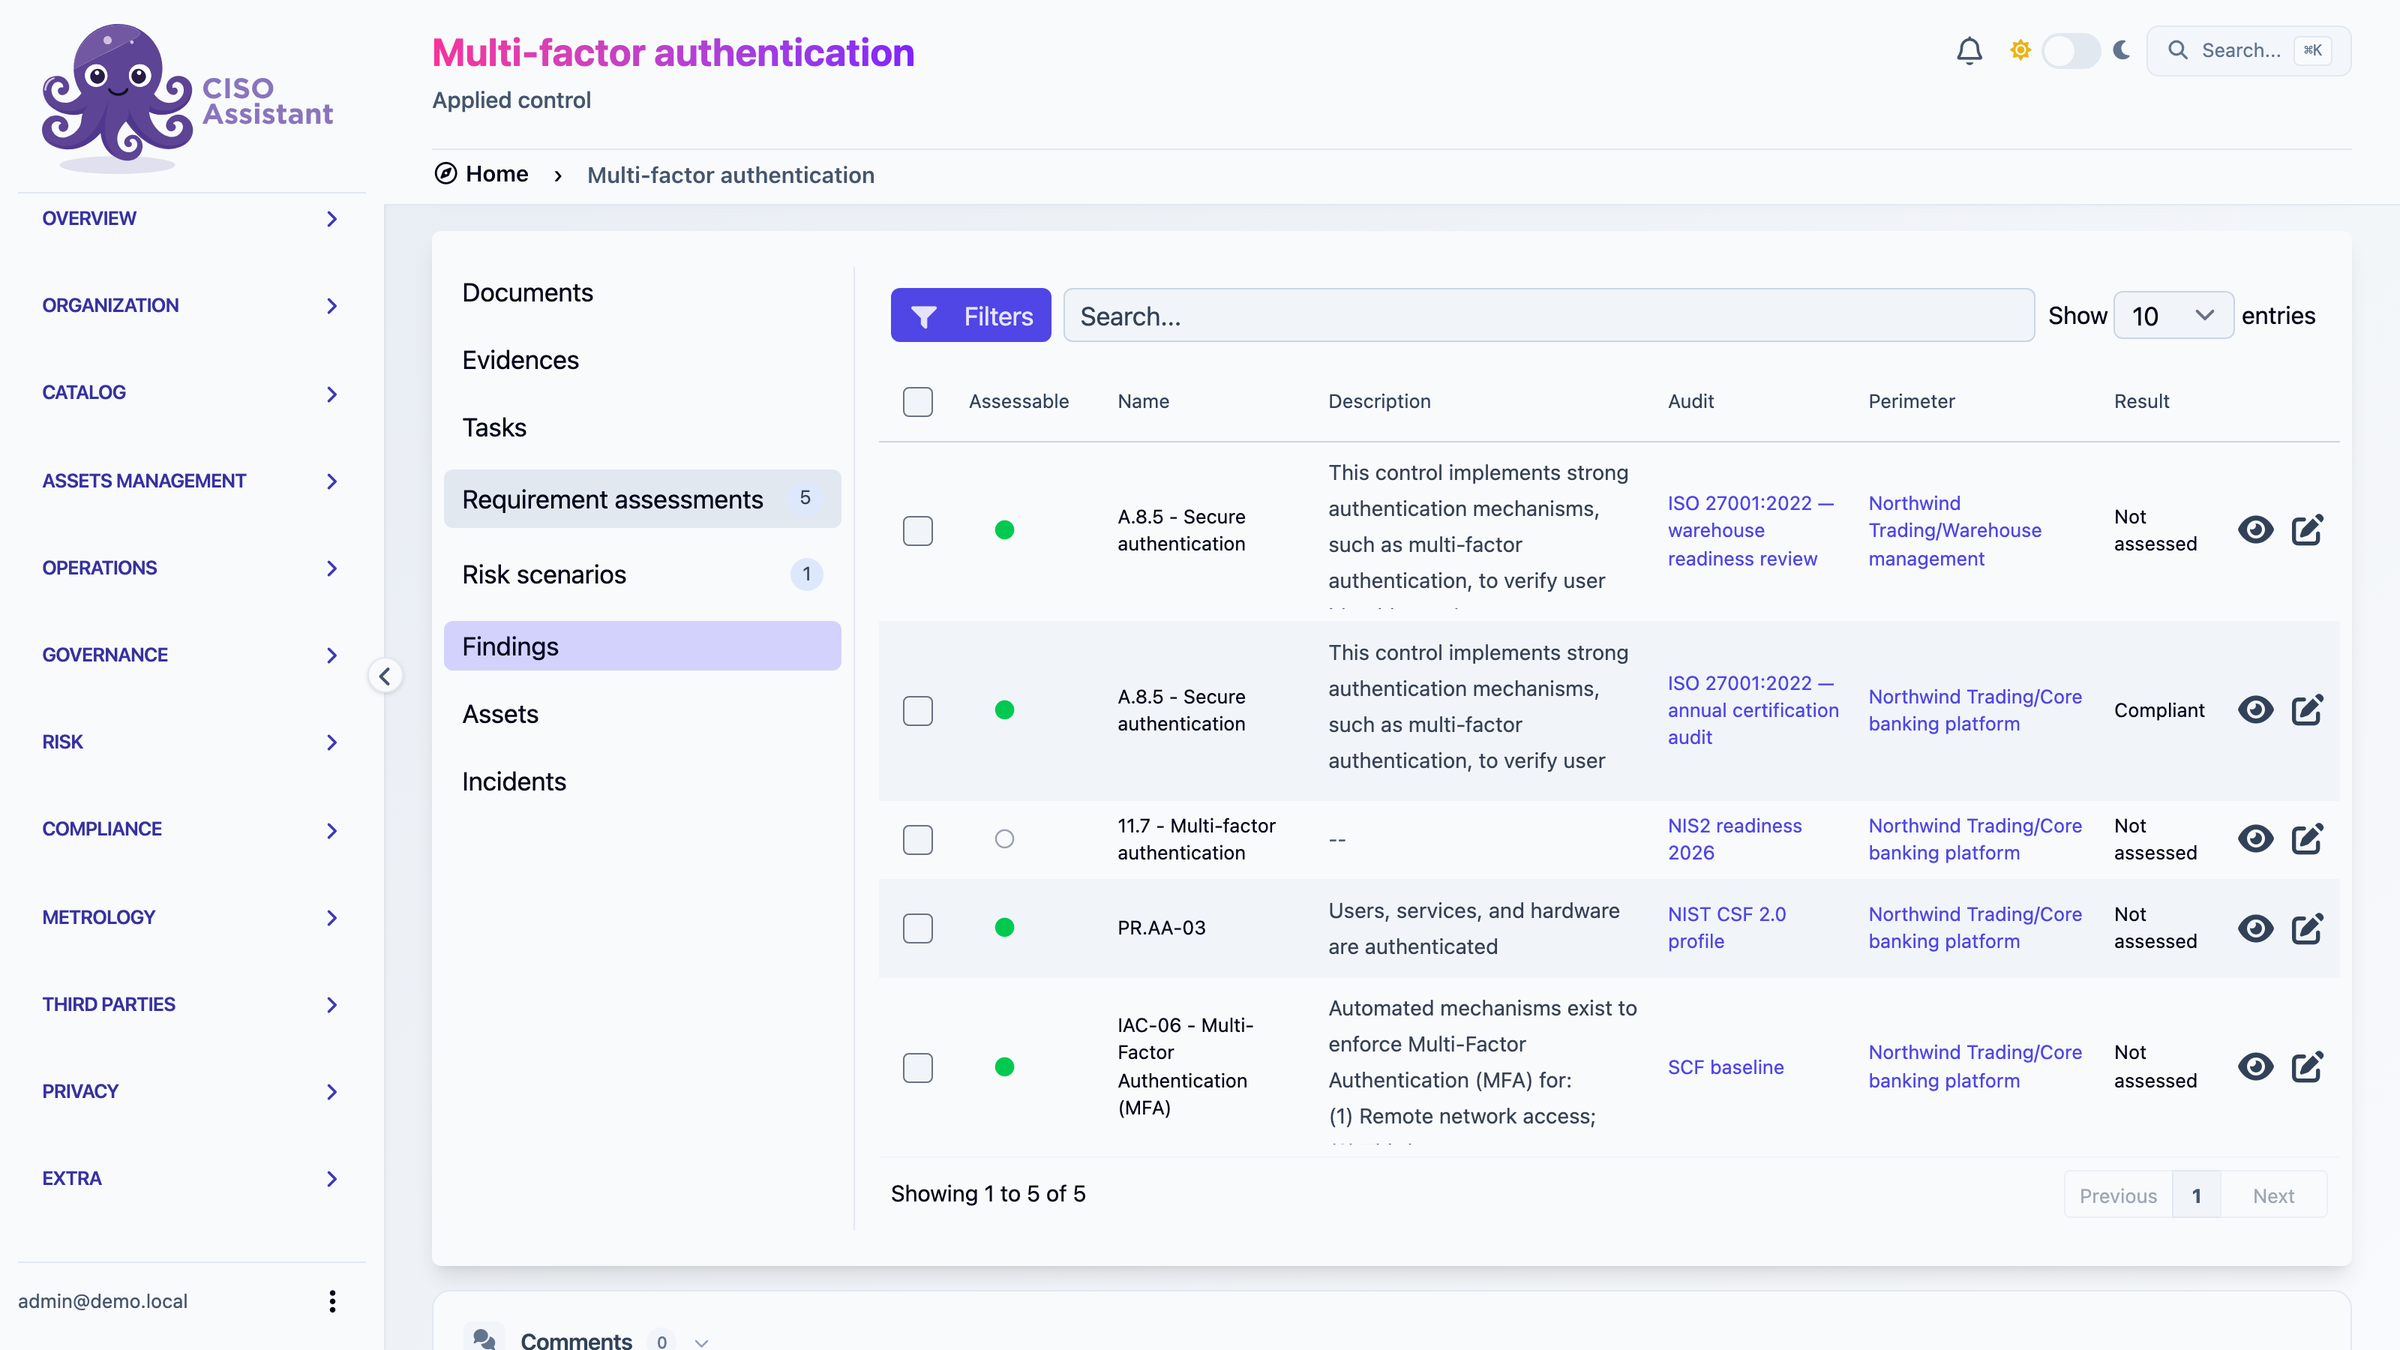
One control, many frameworks
A single multi-factor authentication control answers requirements in ISO 27001, NIS2, NIST CSF 2.0 and the SCF at once.
Applied controls
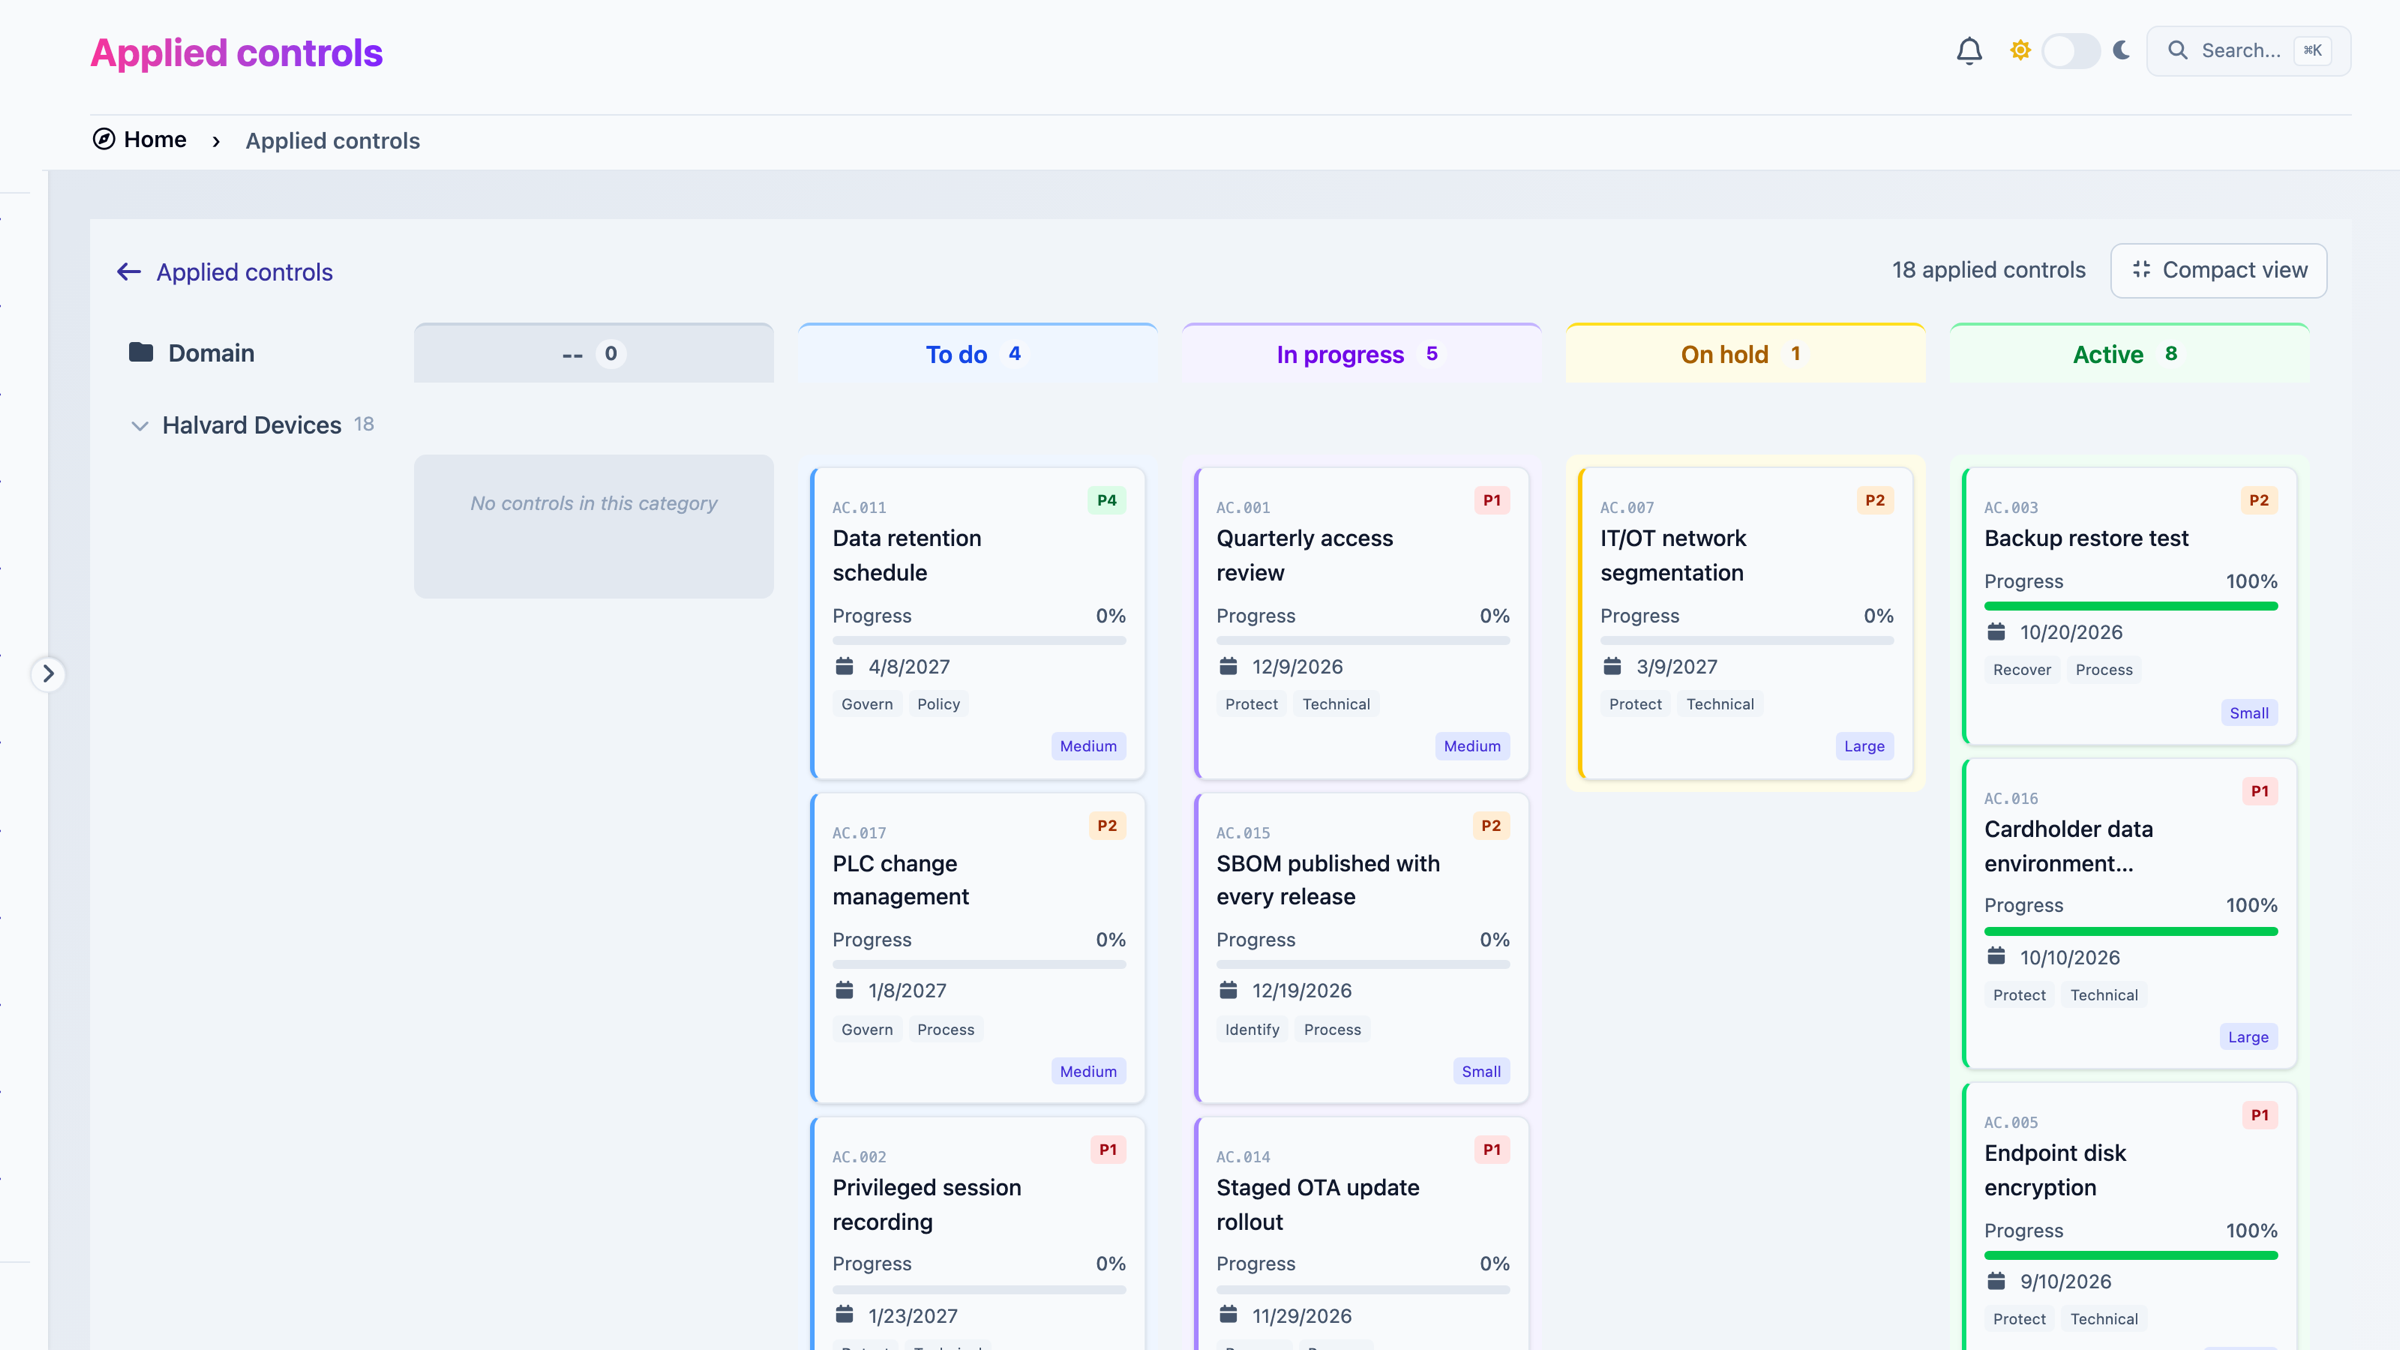
The action plan, in the view that suits you
Every control with its priority, status, owner, ETA, effort and the assets it protects. Work from the filterable table, the kanban board, flash mode or the analytics.
Tasks and evidence
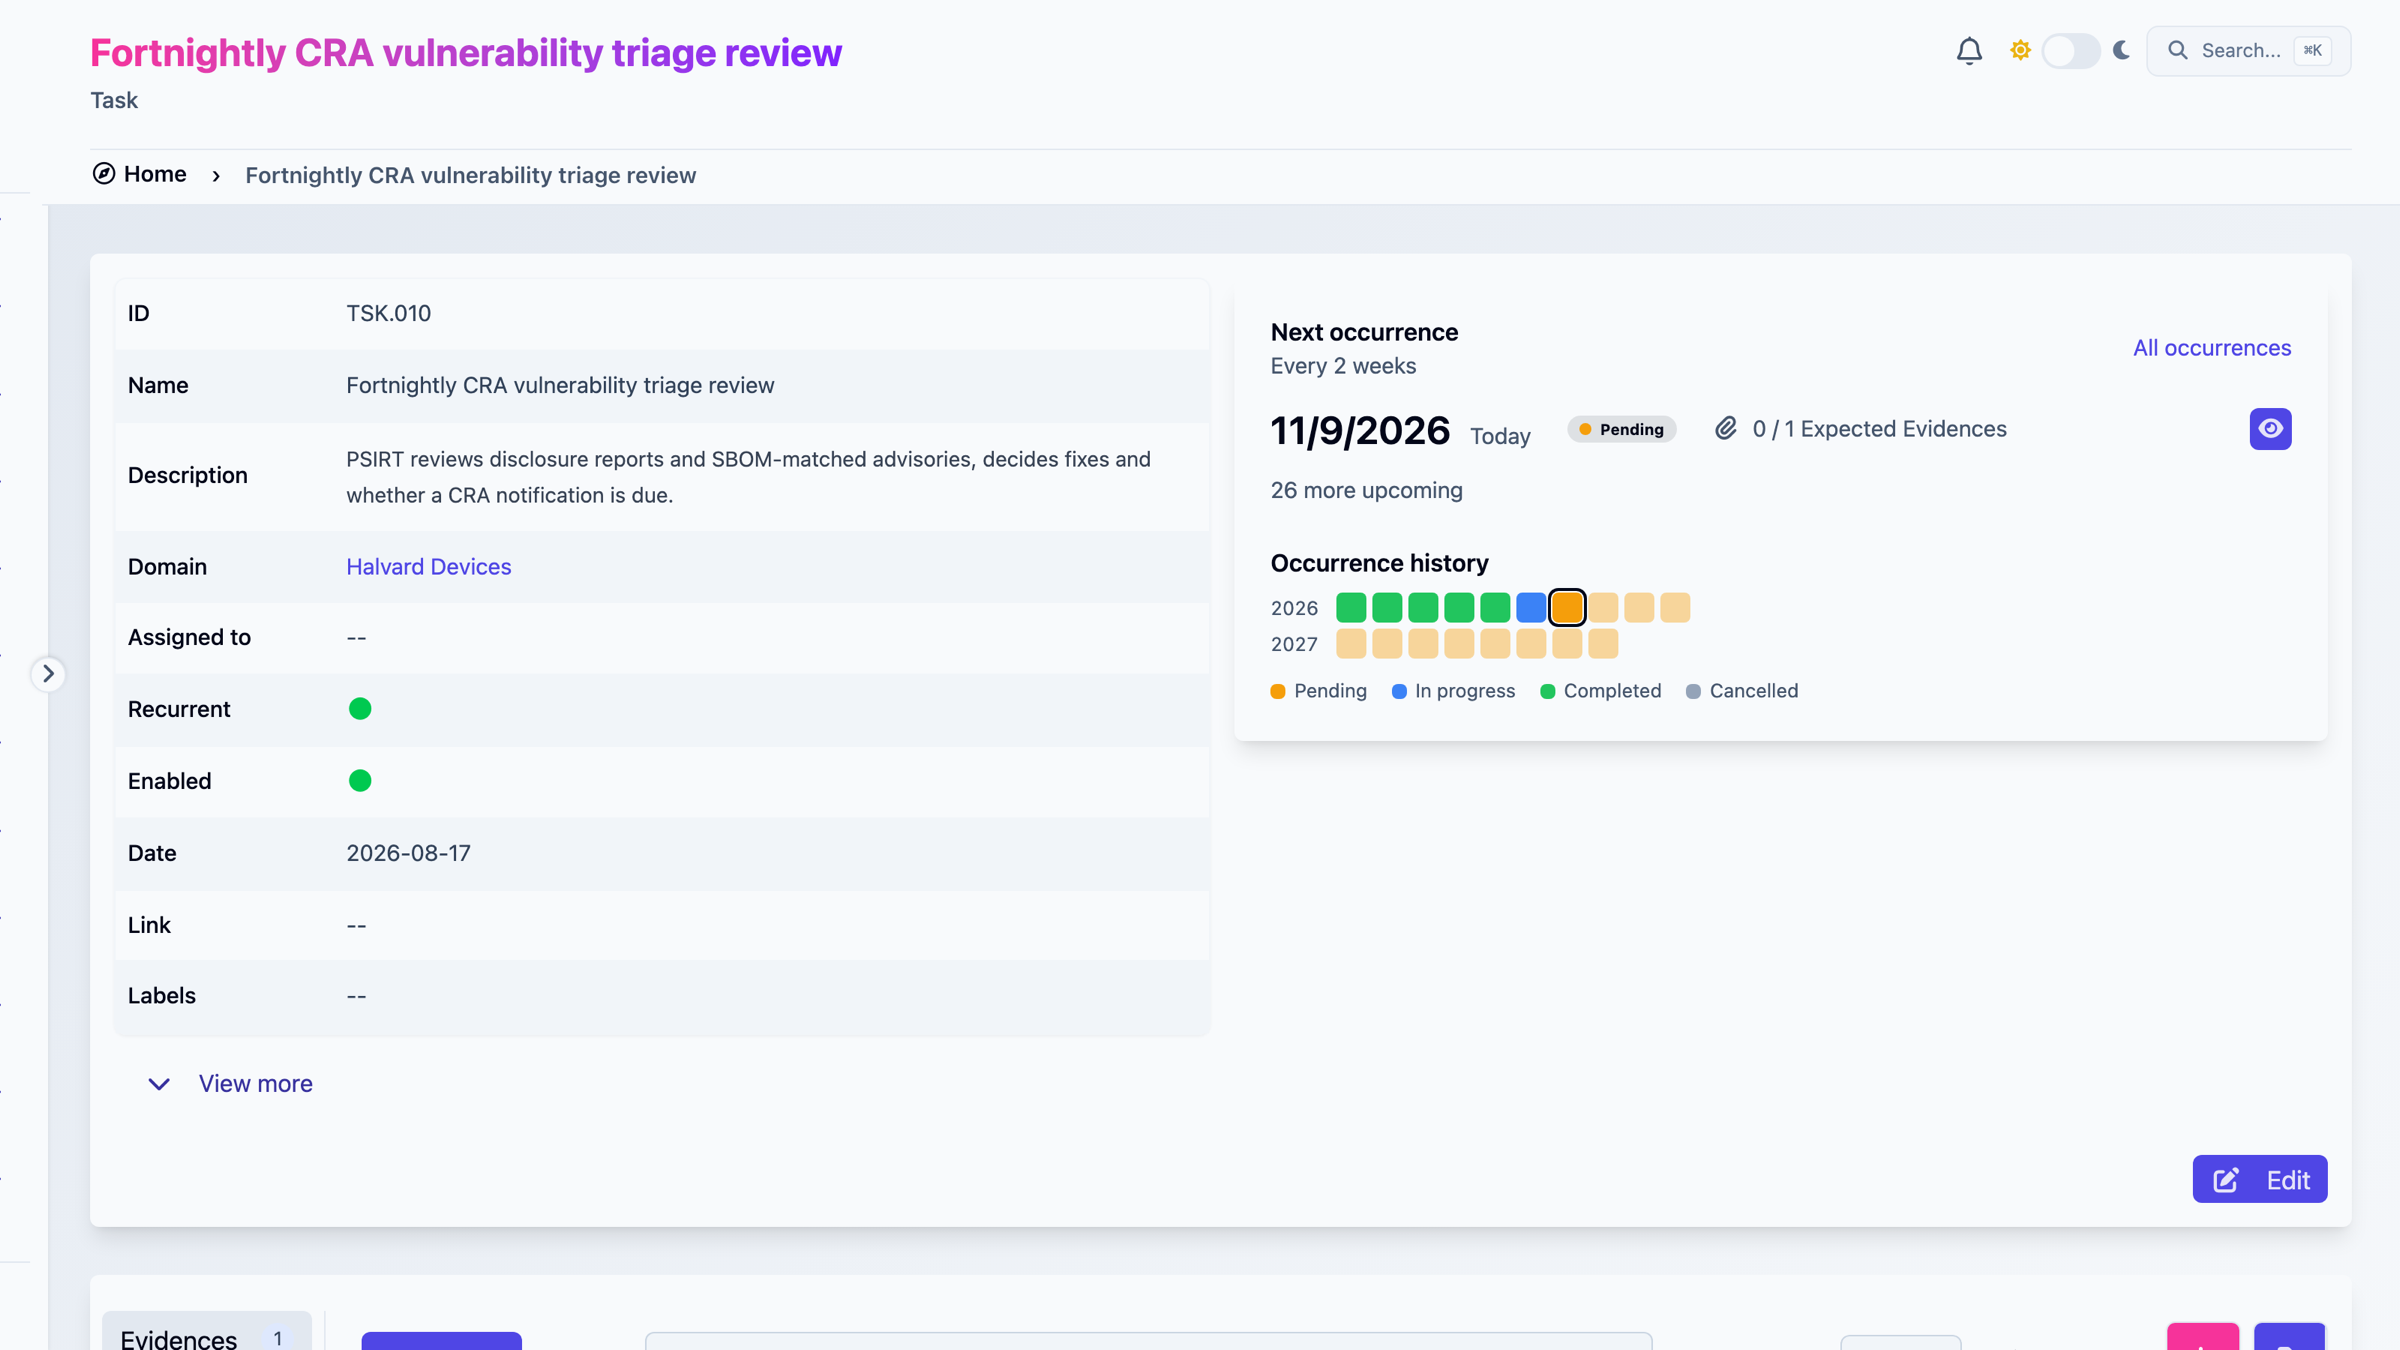
Recurring checks that collect their own evidence
Schedule recurring tasks, every week, month or quarter. Each occurrence asks for the evidence it expects, and the history shows at a glance which ones are completed, pending or cancelled.
Risk assessment
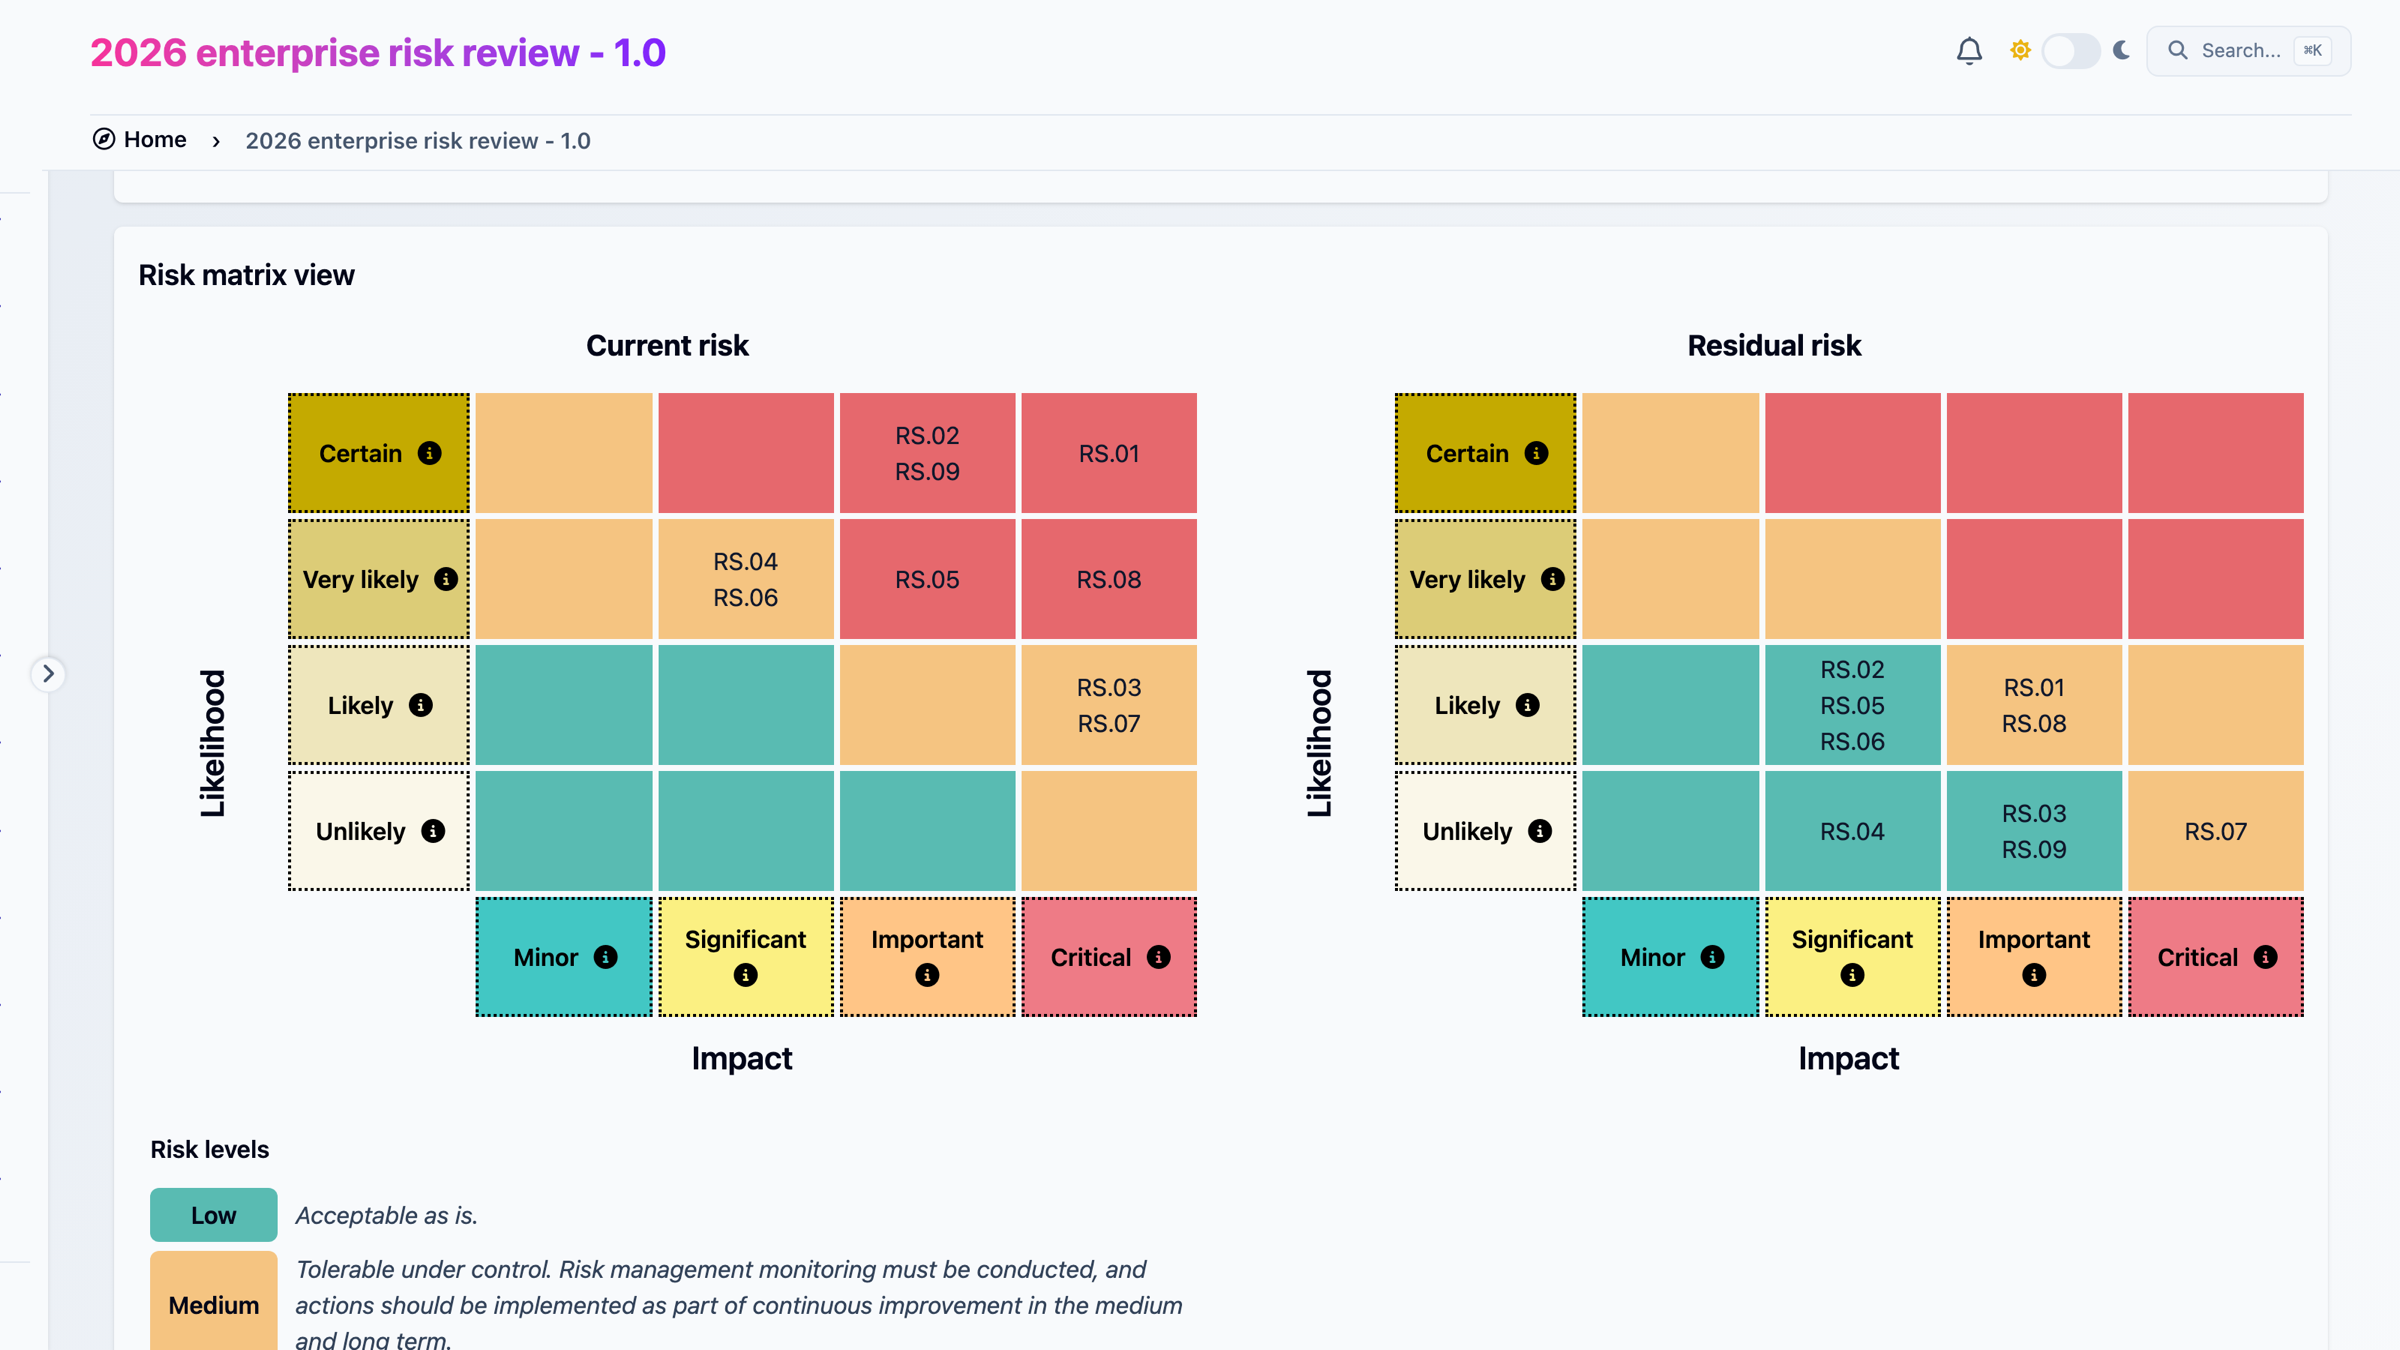
Risk scenarios on the matrix you choose
Every scenario placed on your matrix before and after treatment. Here the EBIOS RM 4×4 grid; ISO 27005 5×5 and your own matrices work the same way.
Quantitative risk
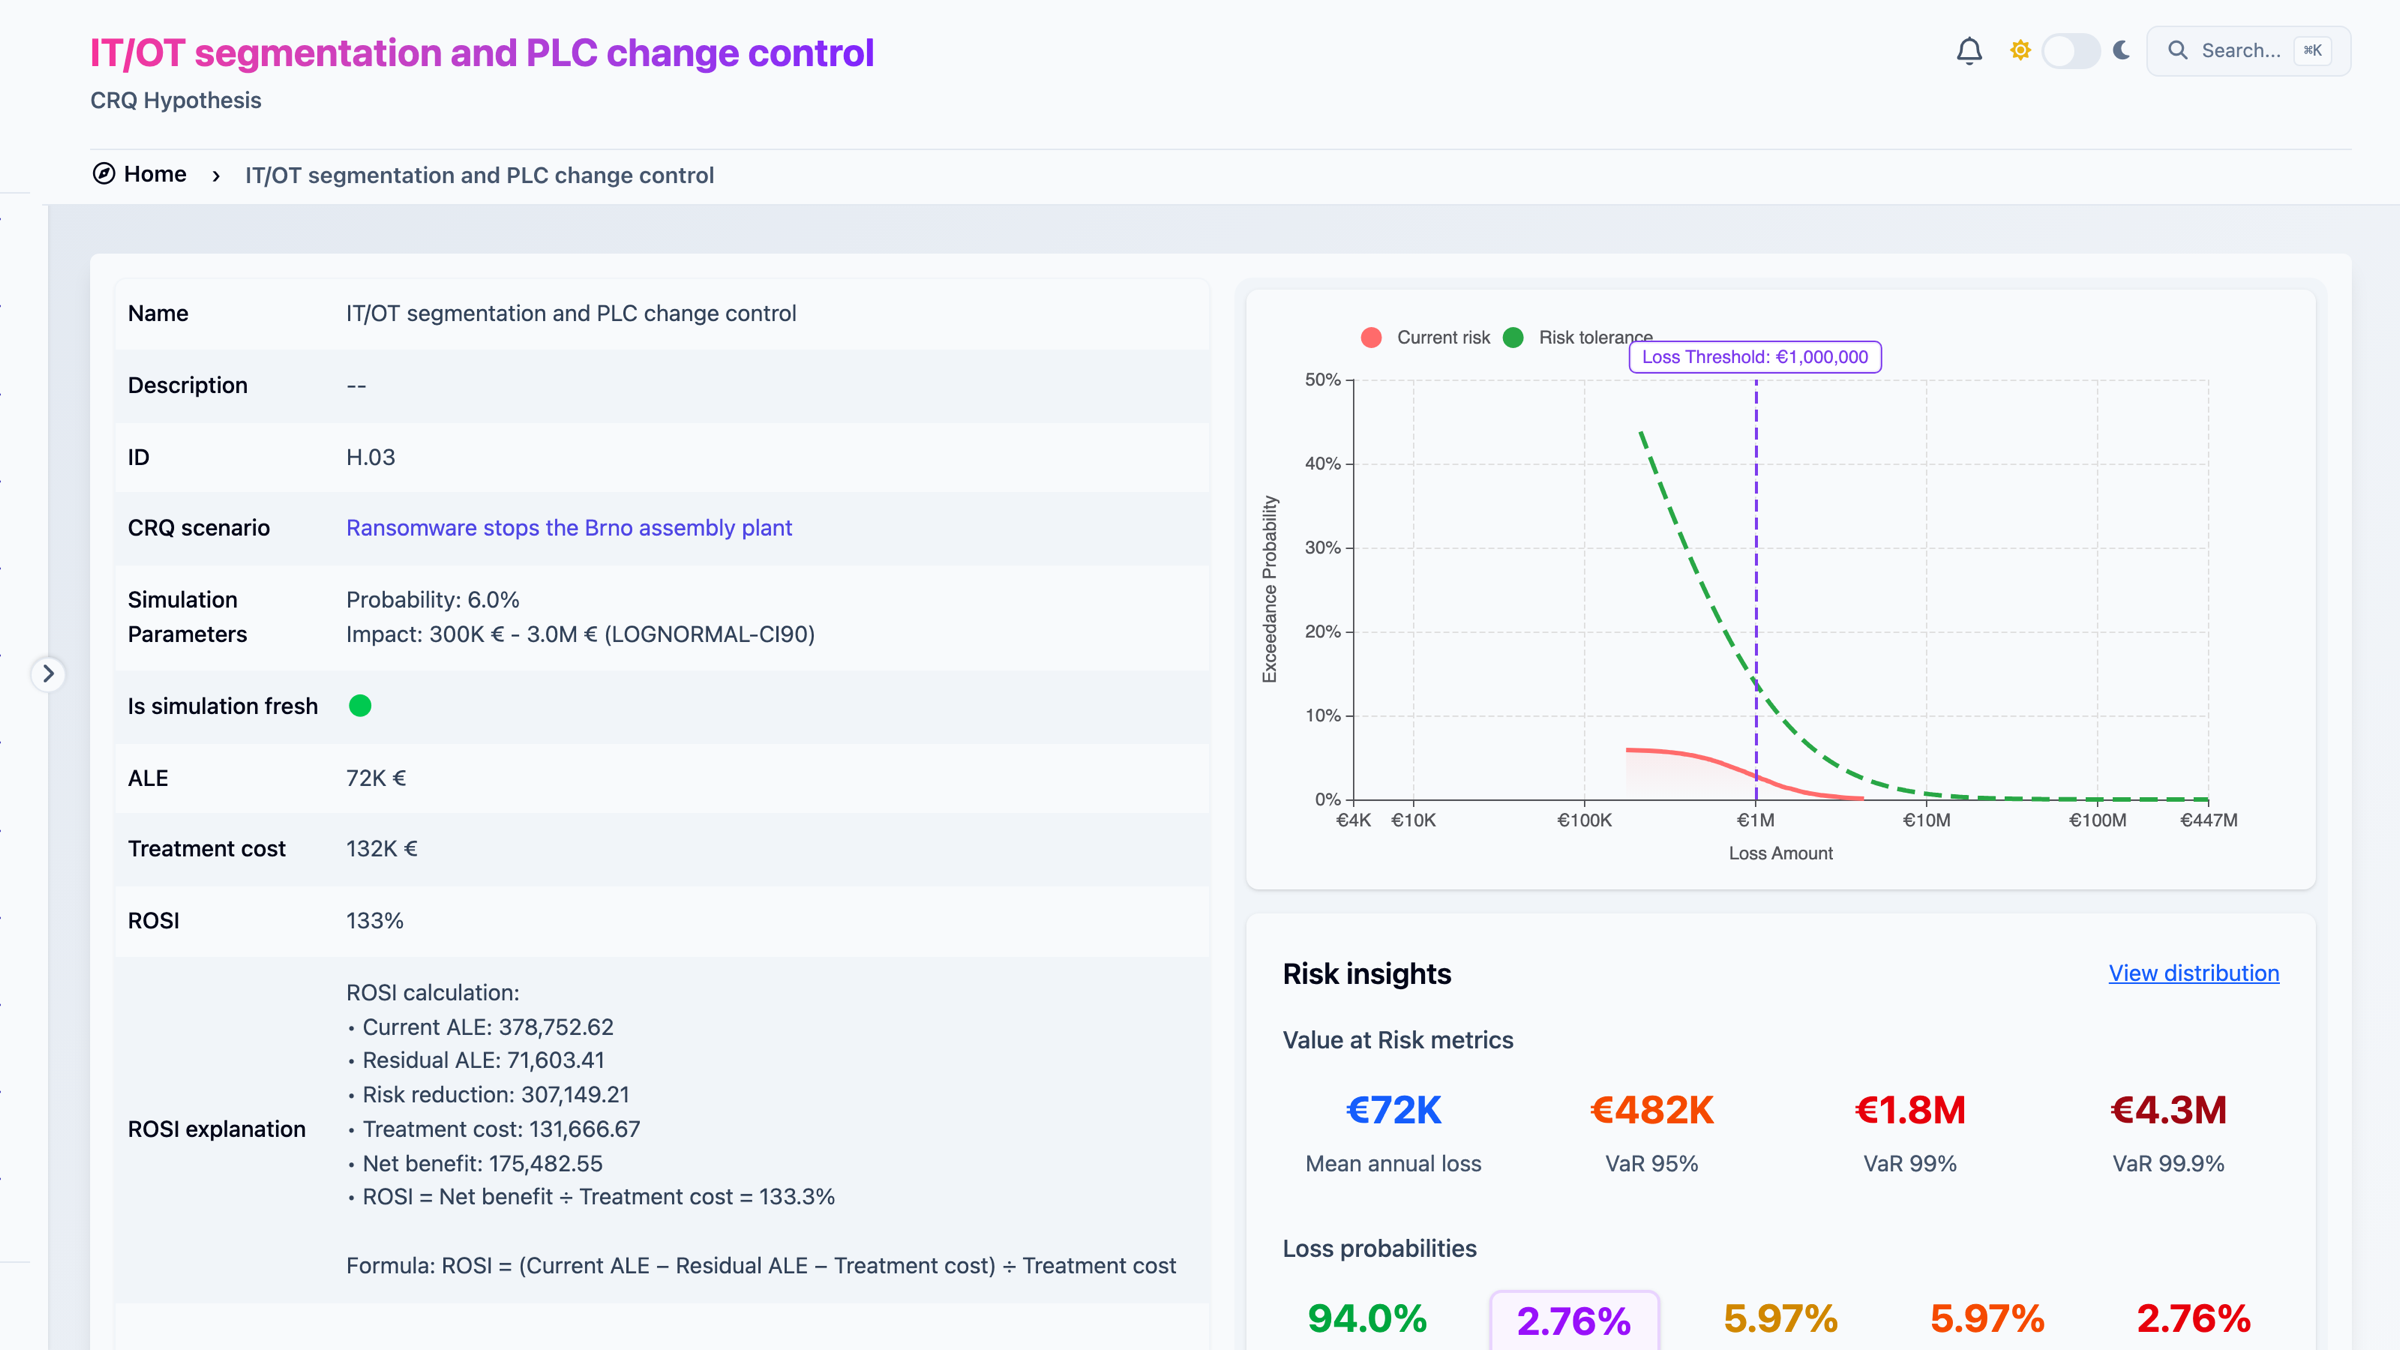
Know what each control is worth
Simulate losses in euros, then compare treatment options by their cost and their return: here, €132K of controls cut the expected annual loss from €379K to €72K, a 133% return on security investment.
EBIOS RM
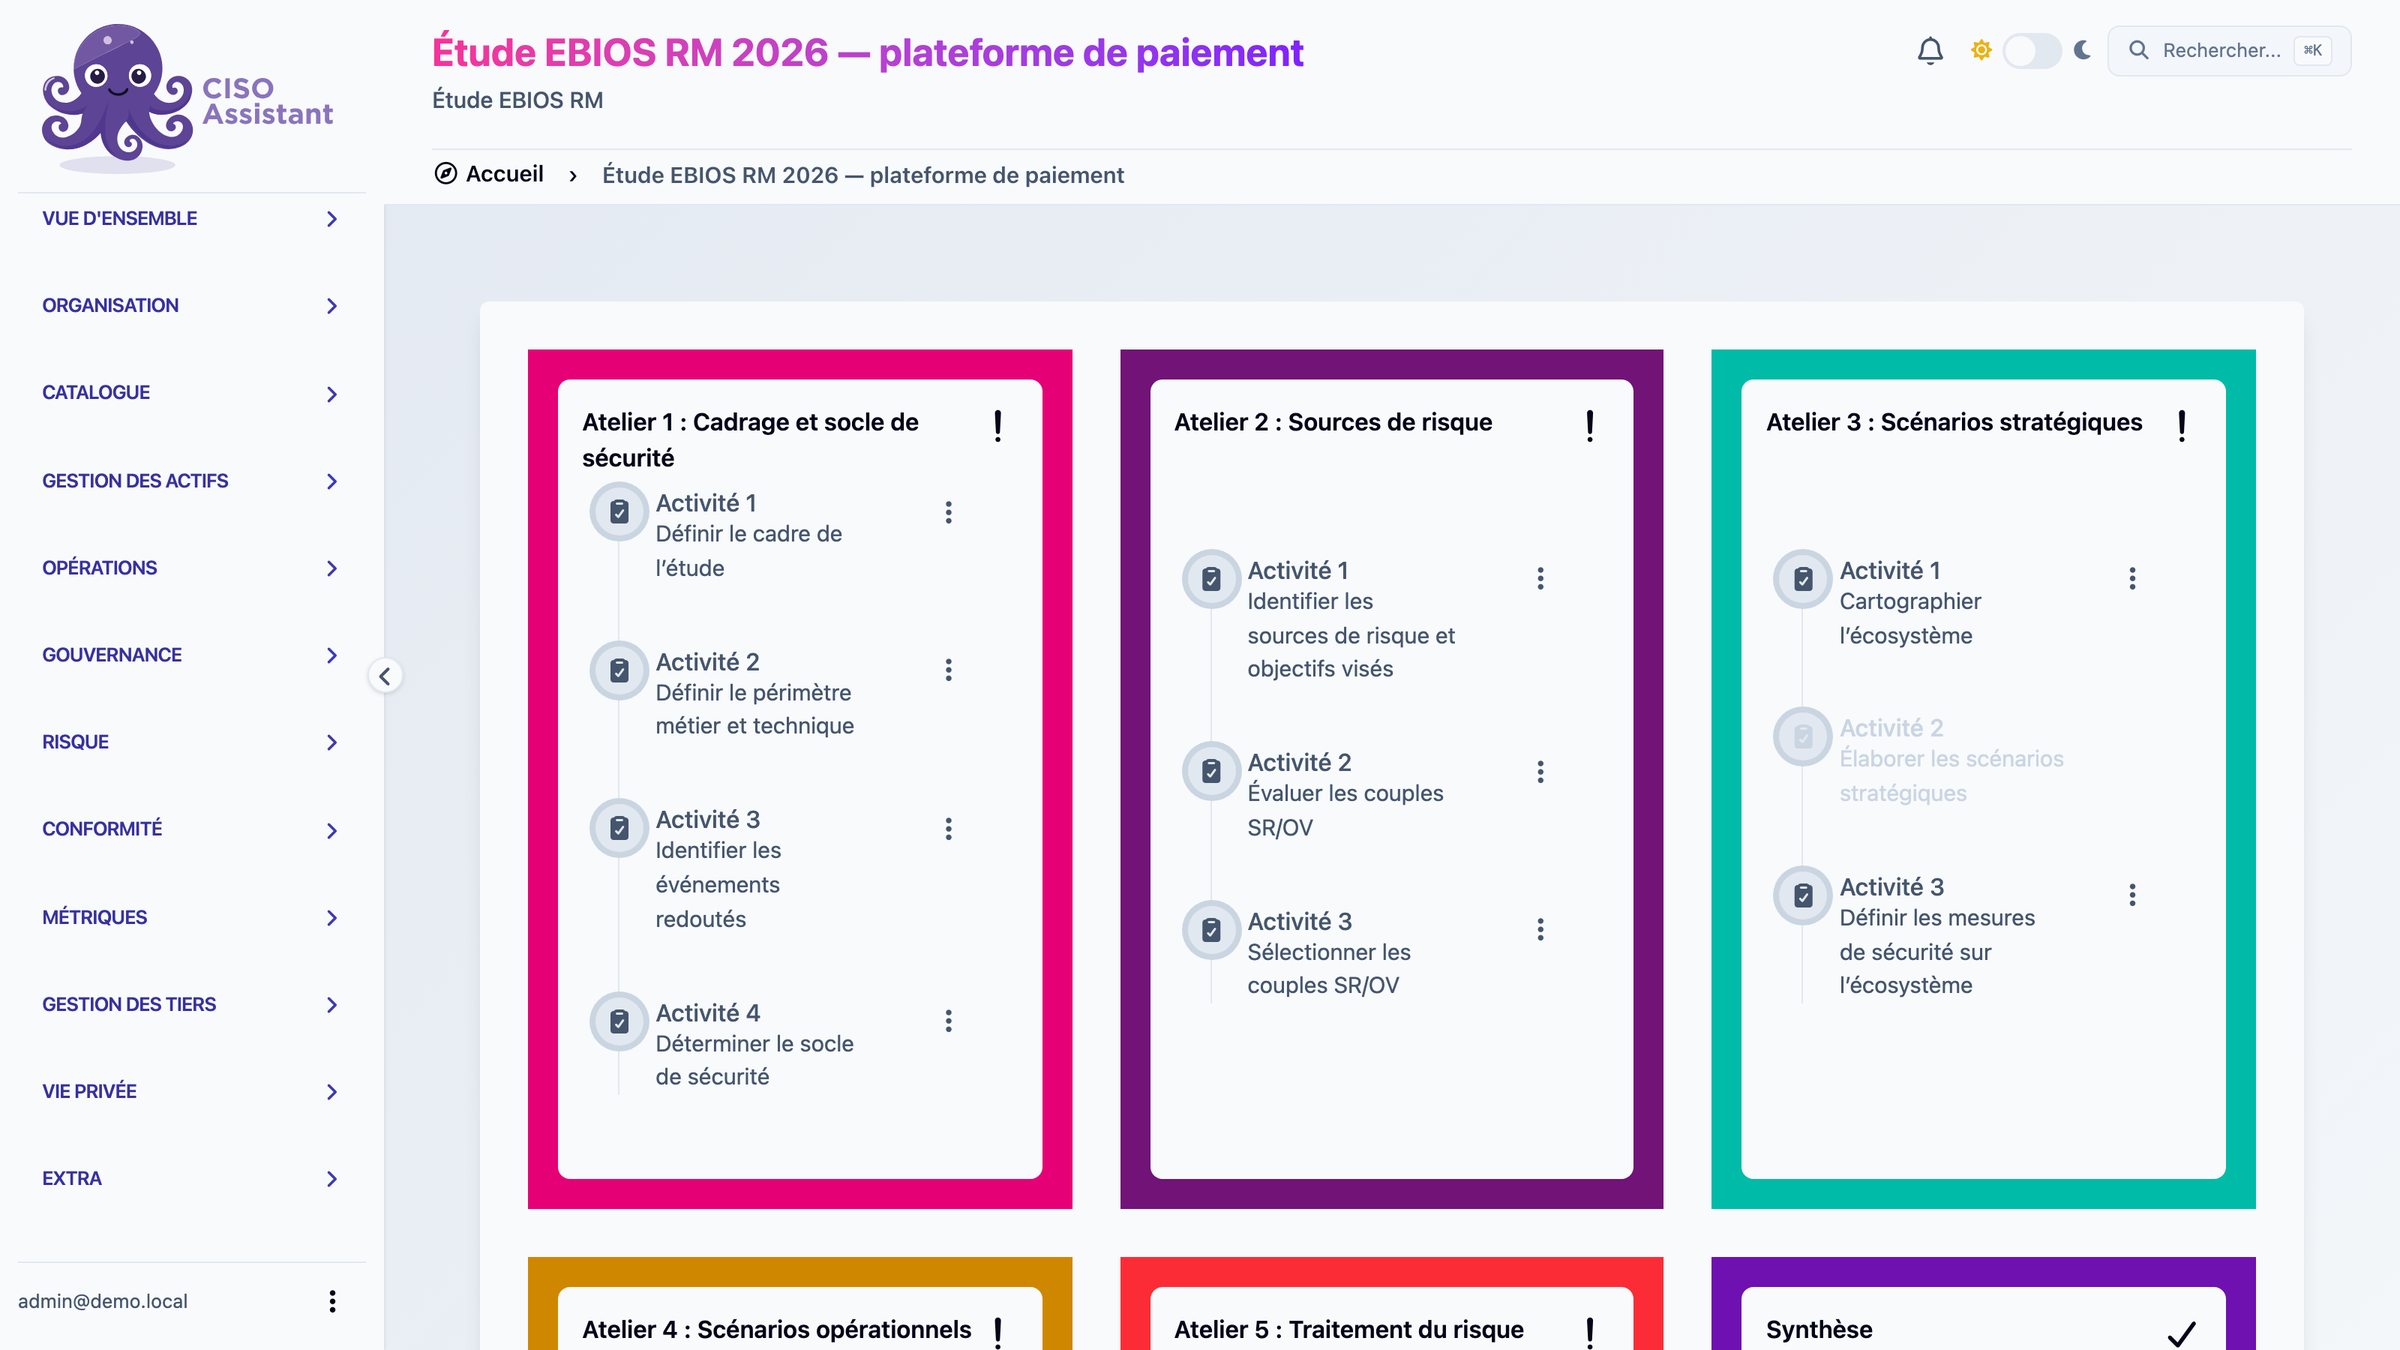
ANSSI's method, workshop by workshop
The five EBIOS RM workshops and their activities in one study, from the security baseline to the risk treatment and its report.
Third parties
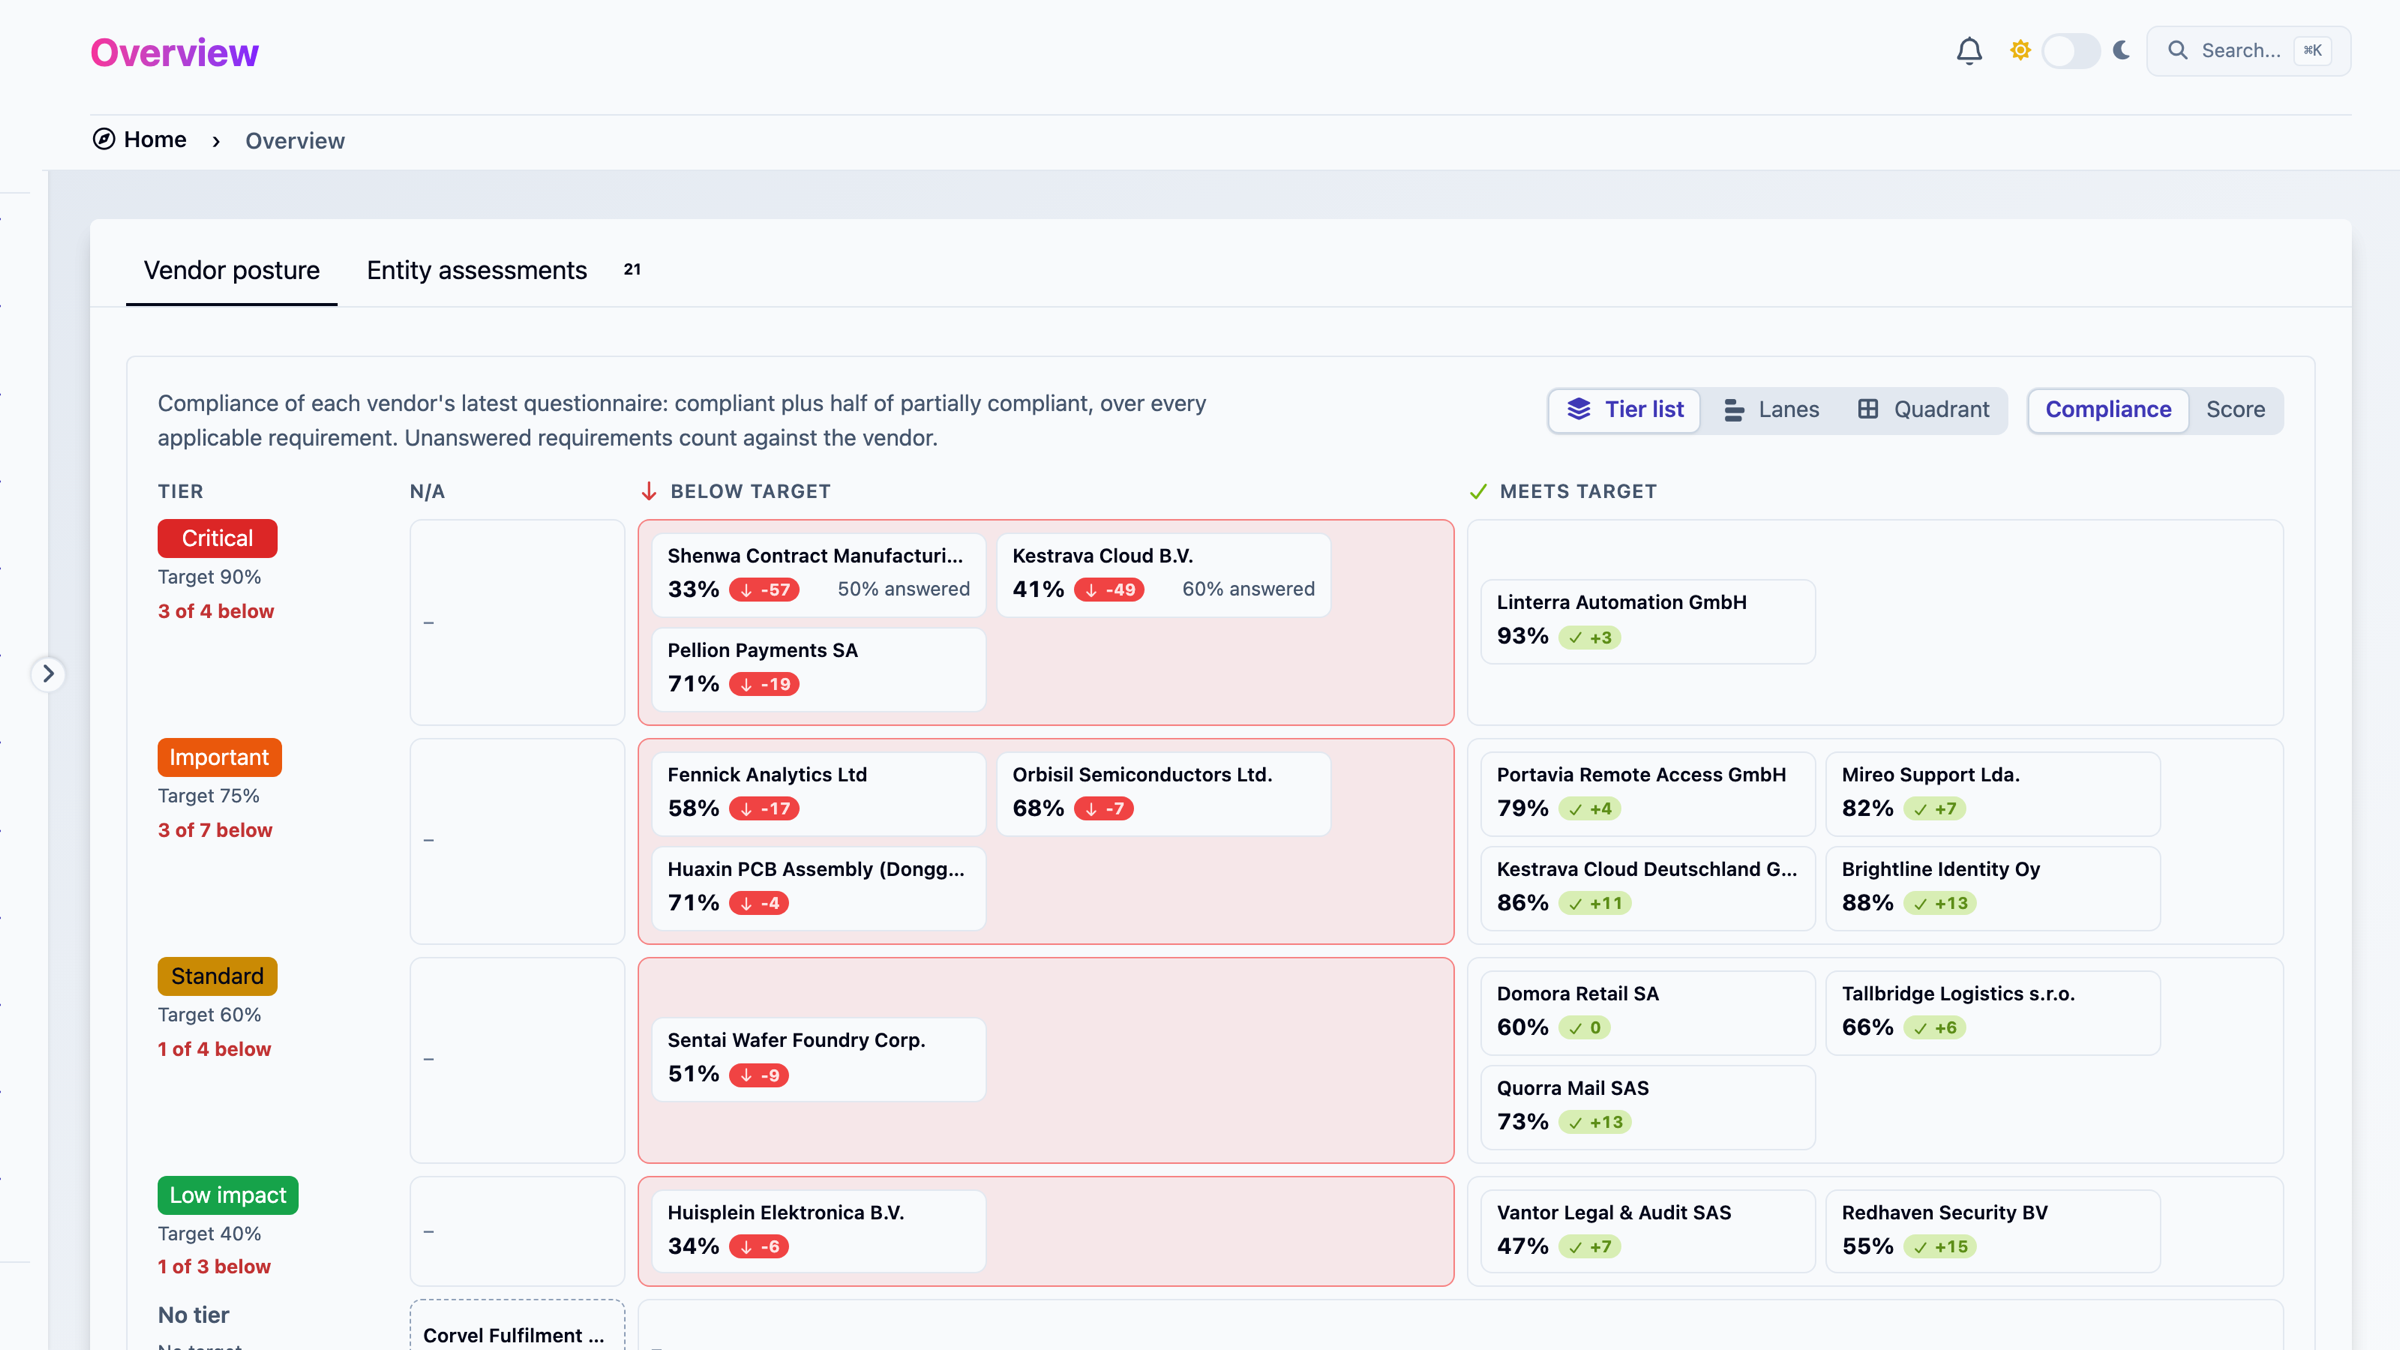
See which vendors fall short
Rank third parties on your own criticality scale, set a compliance target per tier and see at a glance which vendors are below it, in a tier list, lanes or a quadrant.
Vendor questionnaires
Vendors answer in their own portal
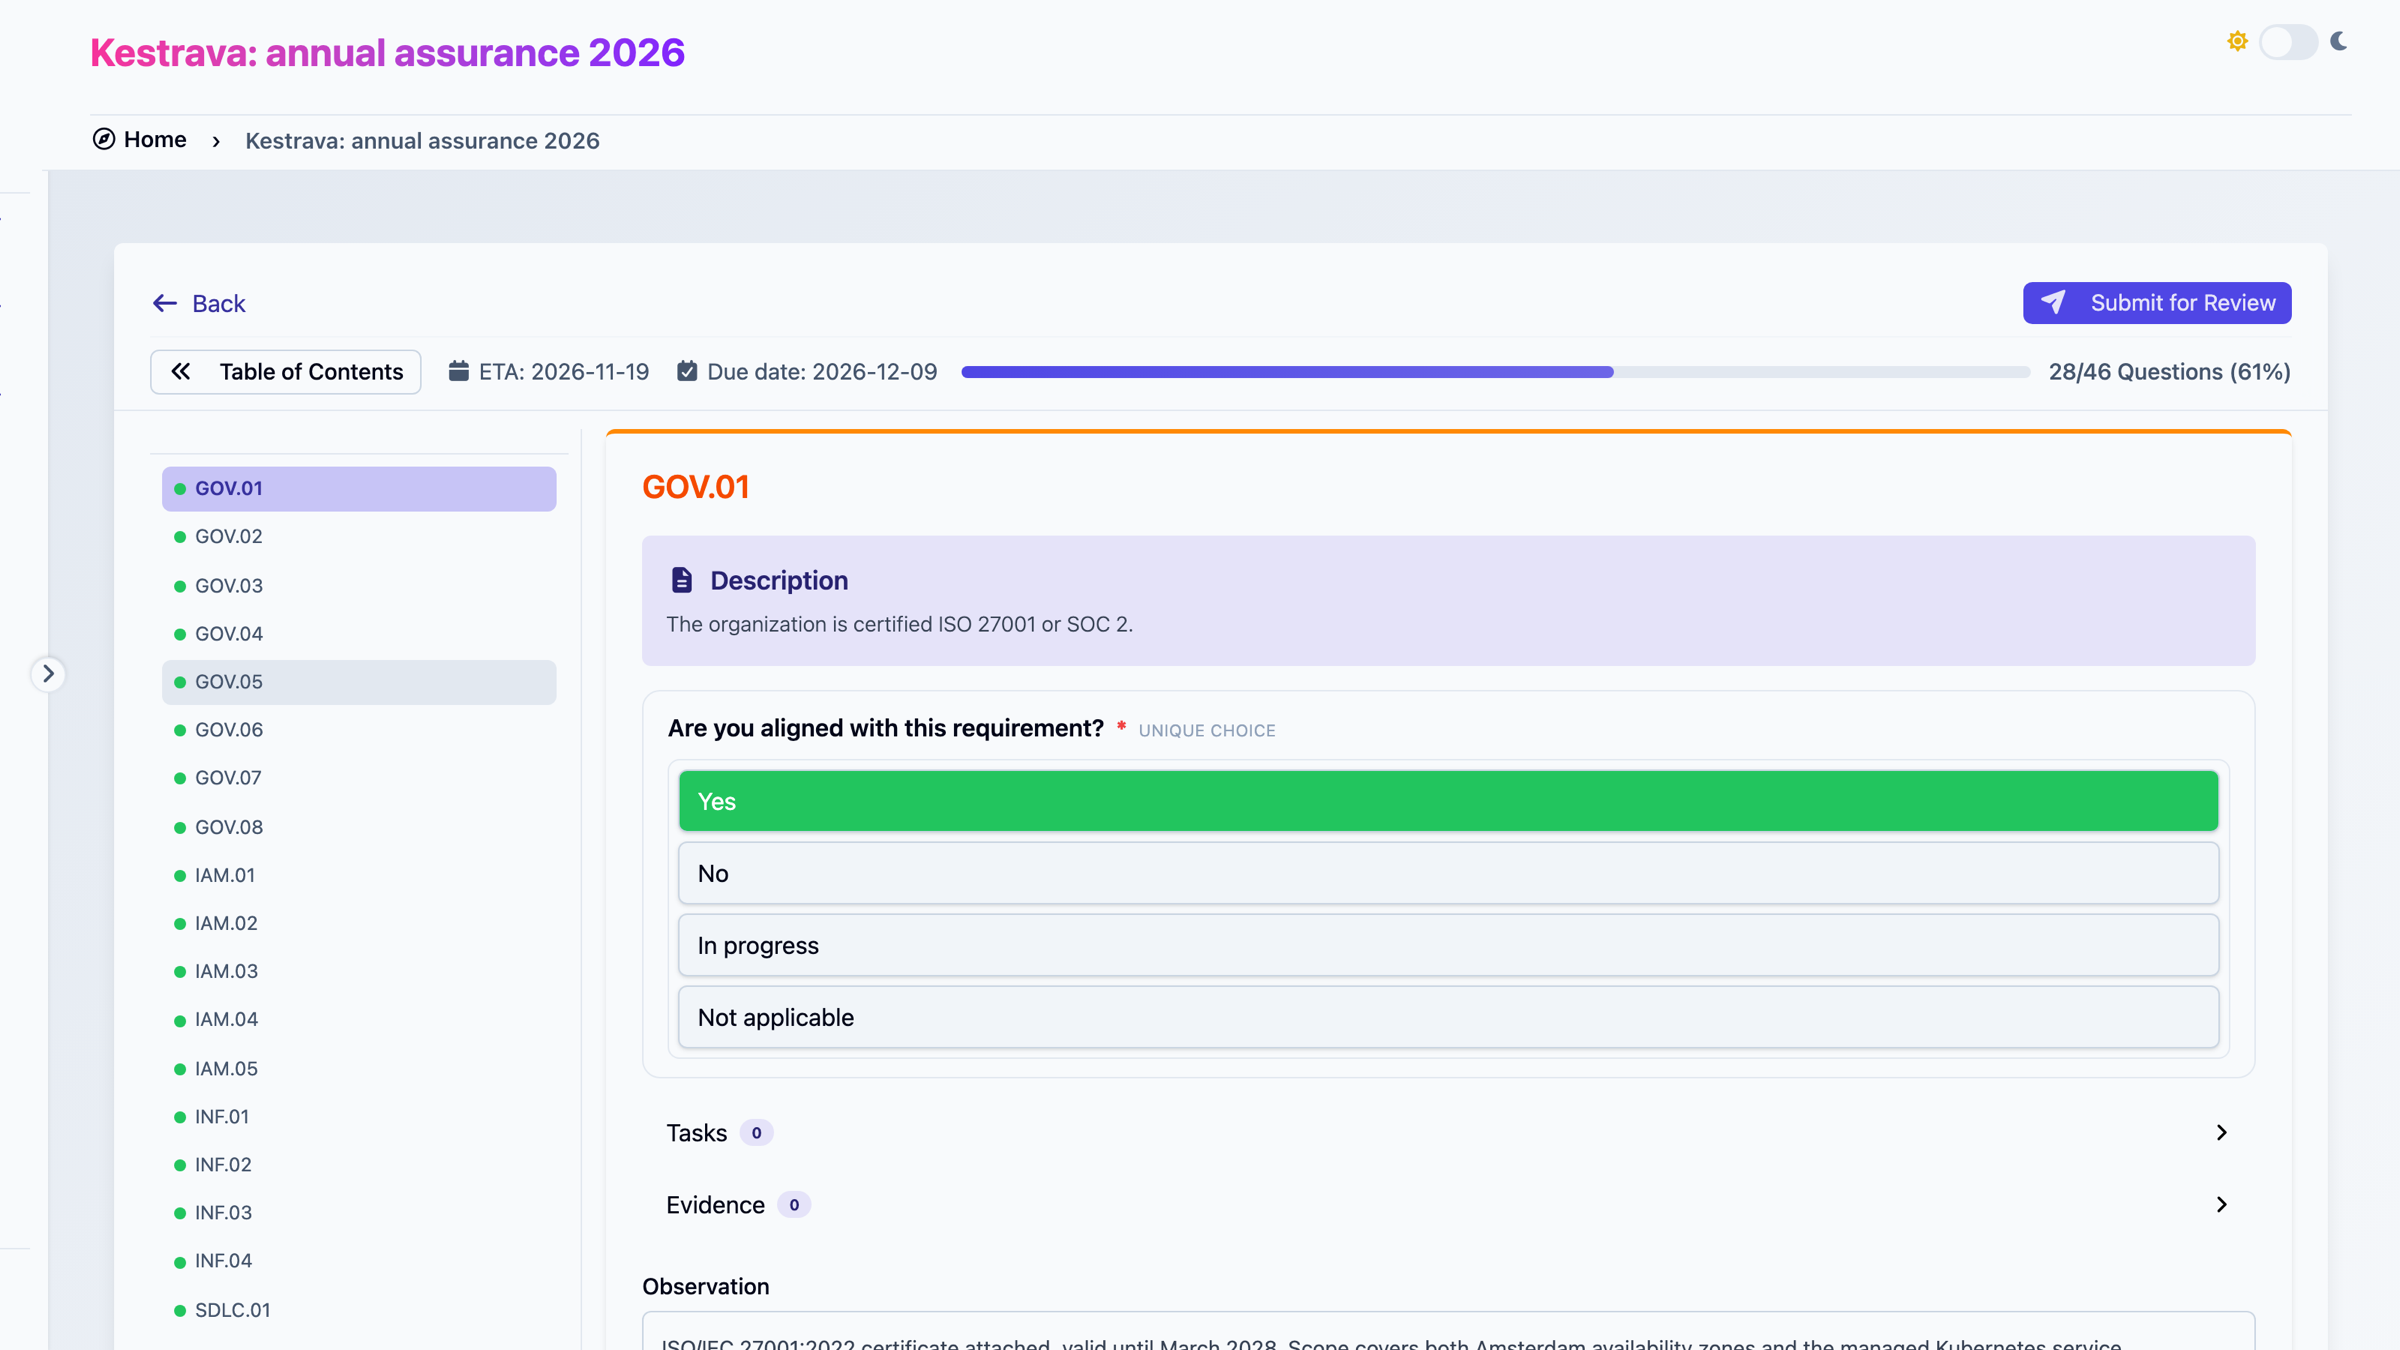
Each third party gets its own access to the questionnaires sent to it: it answers question by question, attaches evidence and submits for review. Your team then reviews the answers and turns the gaps into an action plan.
DORA
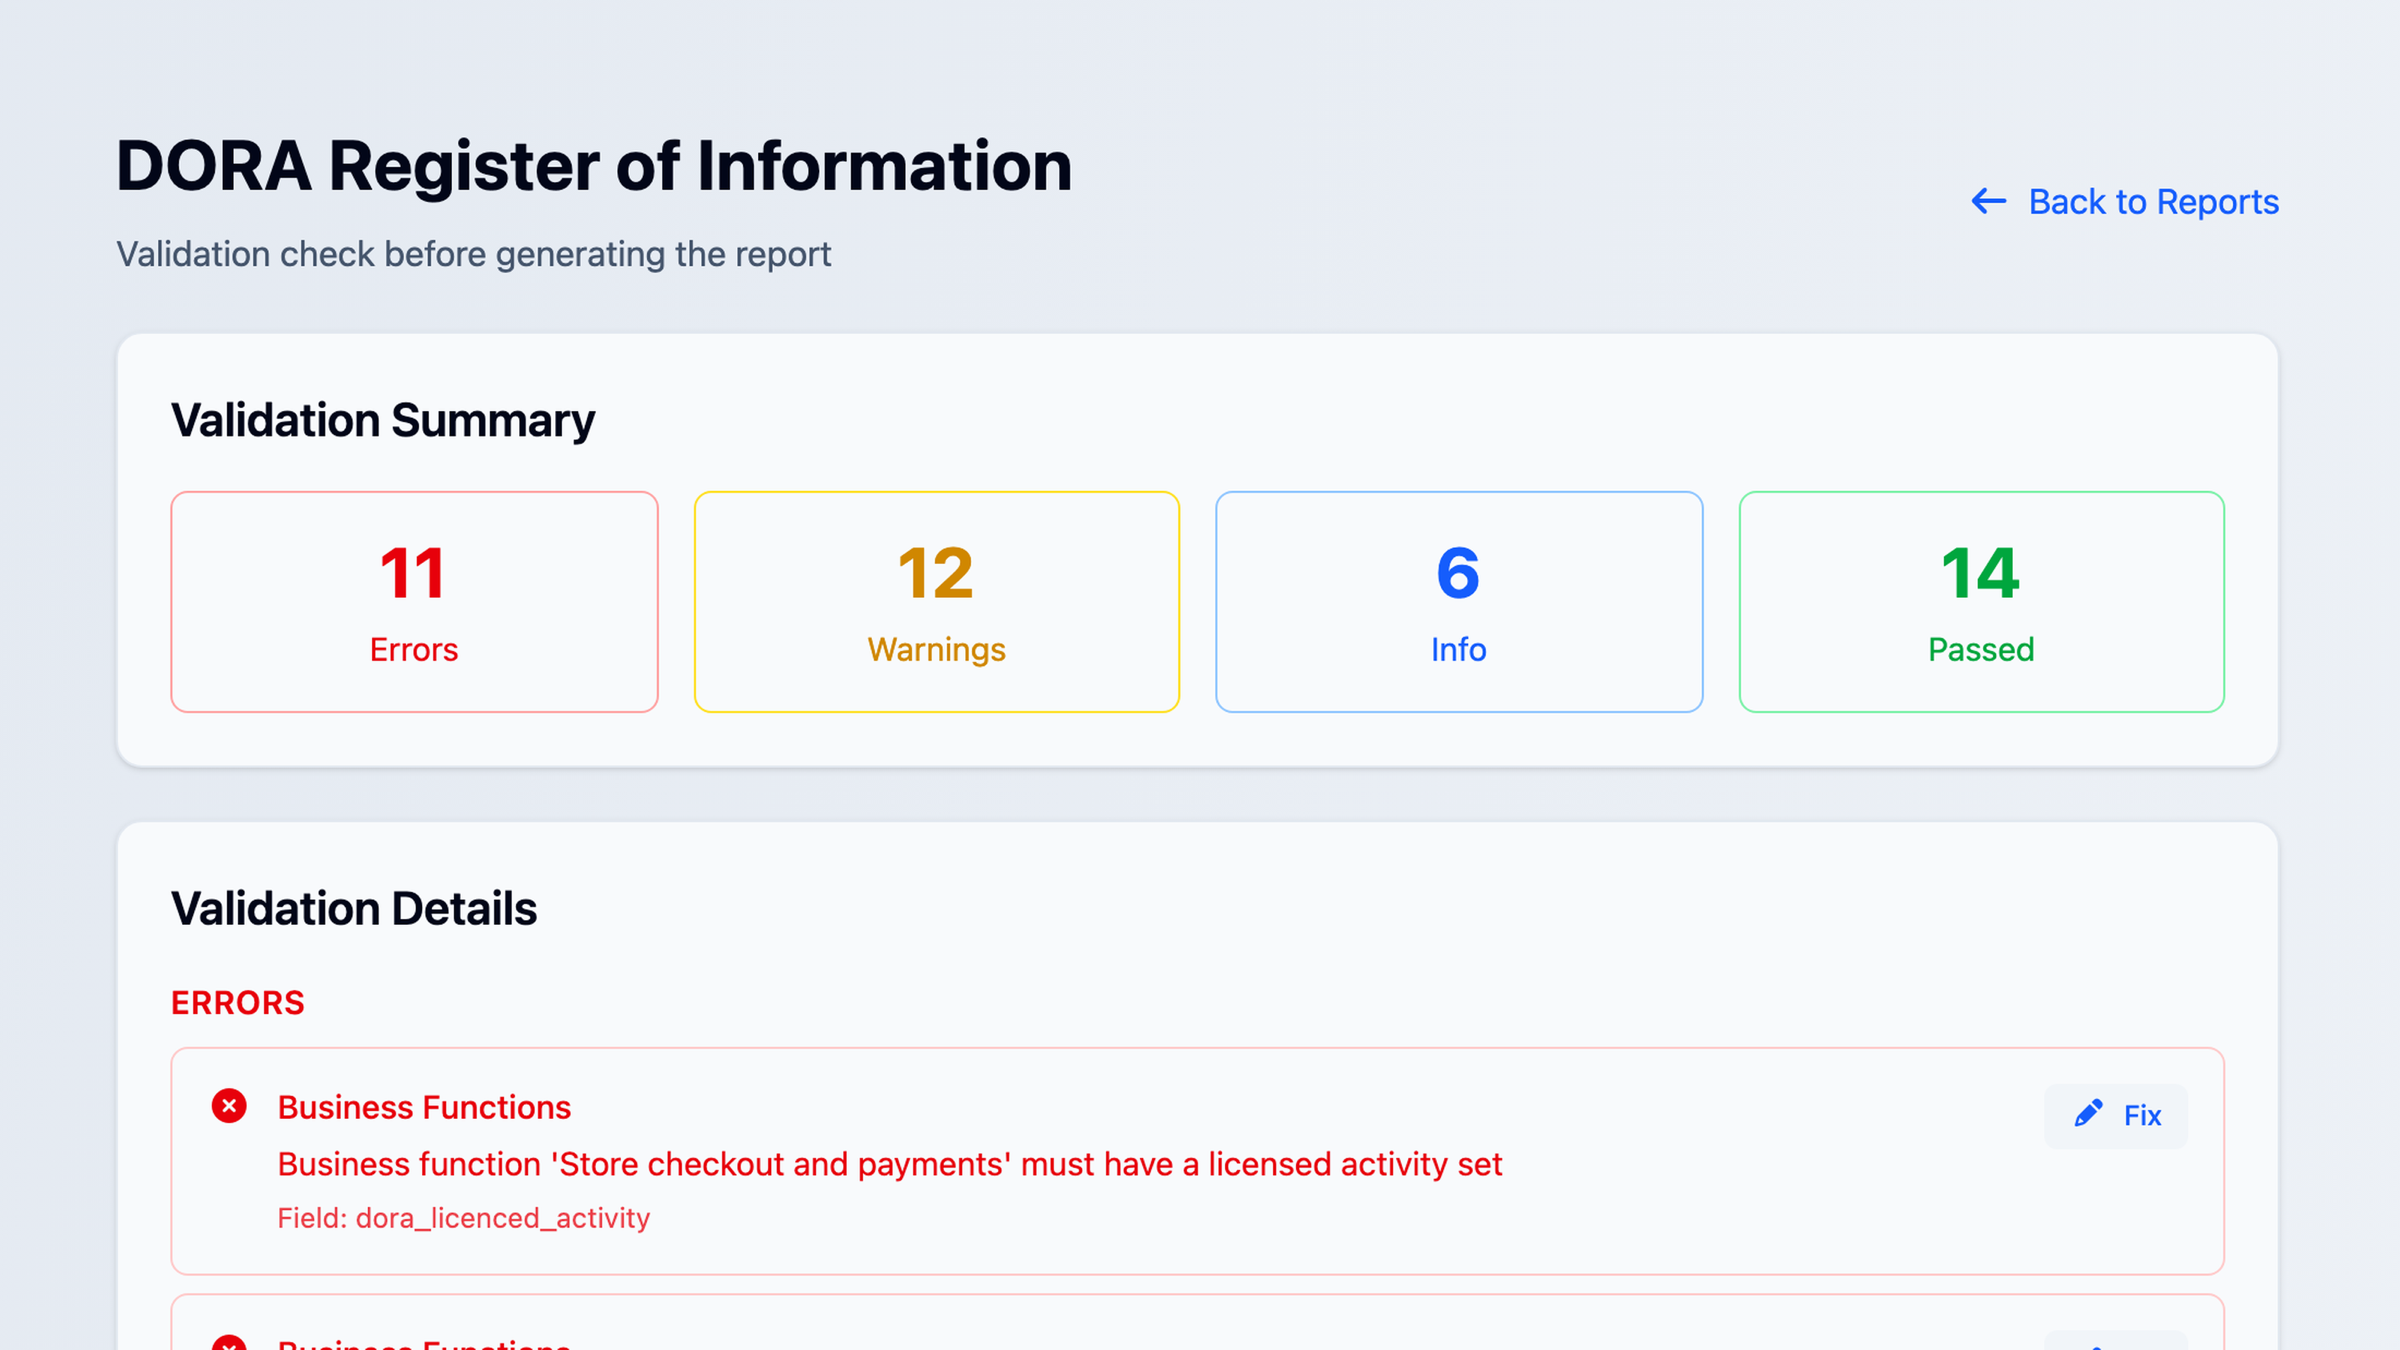
Your DORA Register of Information, checked before you file
Your vendors, contracts and ICT services become the DORA Register of Information. A validation pass flags every missing field before export, with a link to fix each one.
Privacy
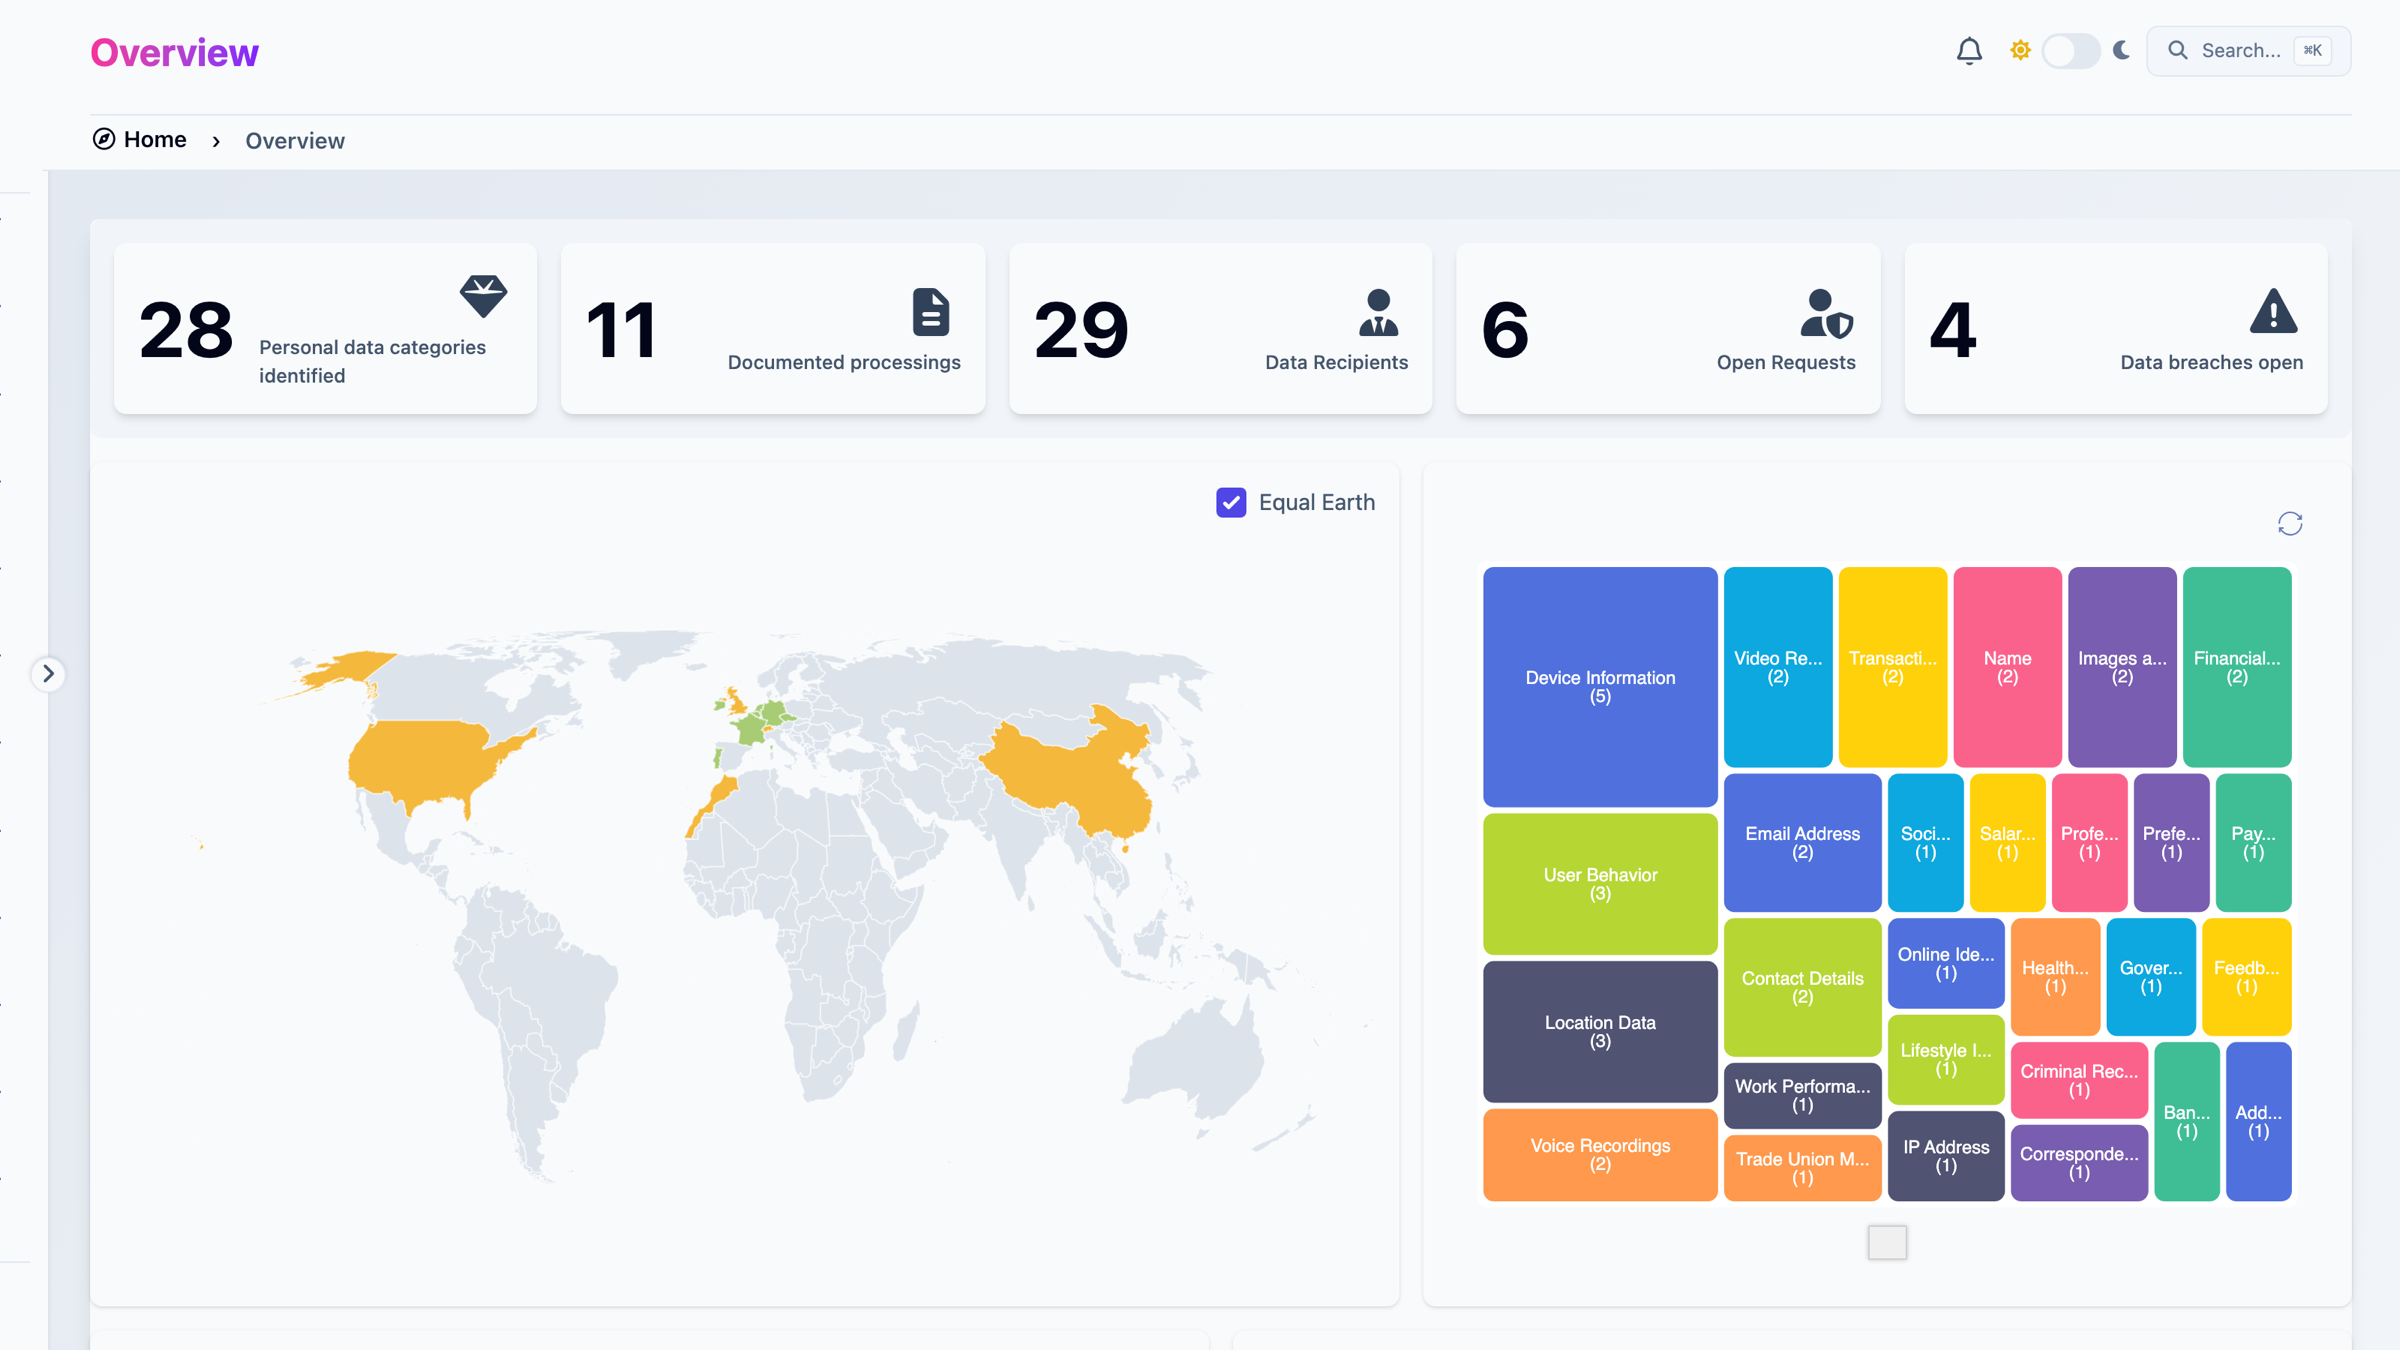
Your GDPR register, at a glance
Processings, personal data categories, recipients and transfers outside the EU, data subject requests, breaches and DPIAs, kept in the same tool as the rest of your program.
Workflows
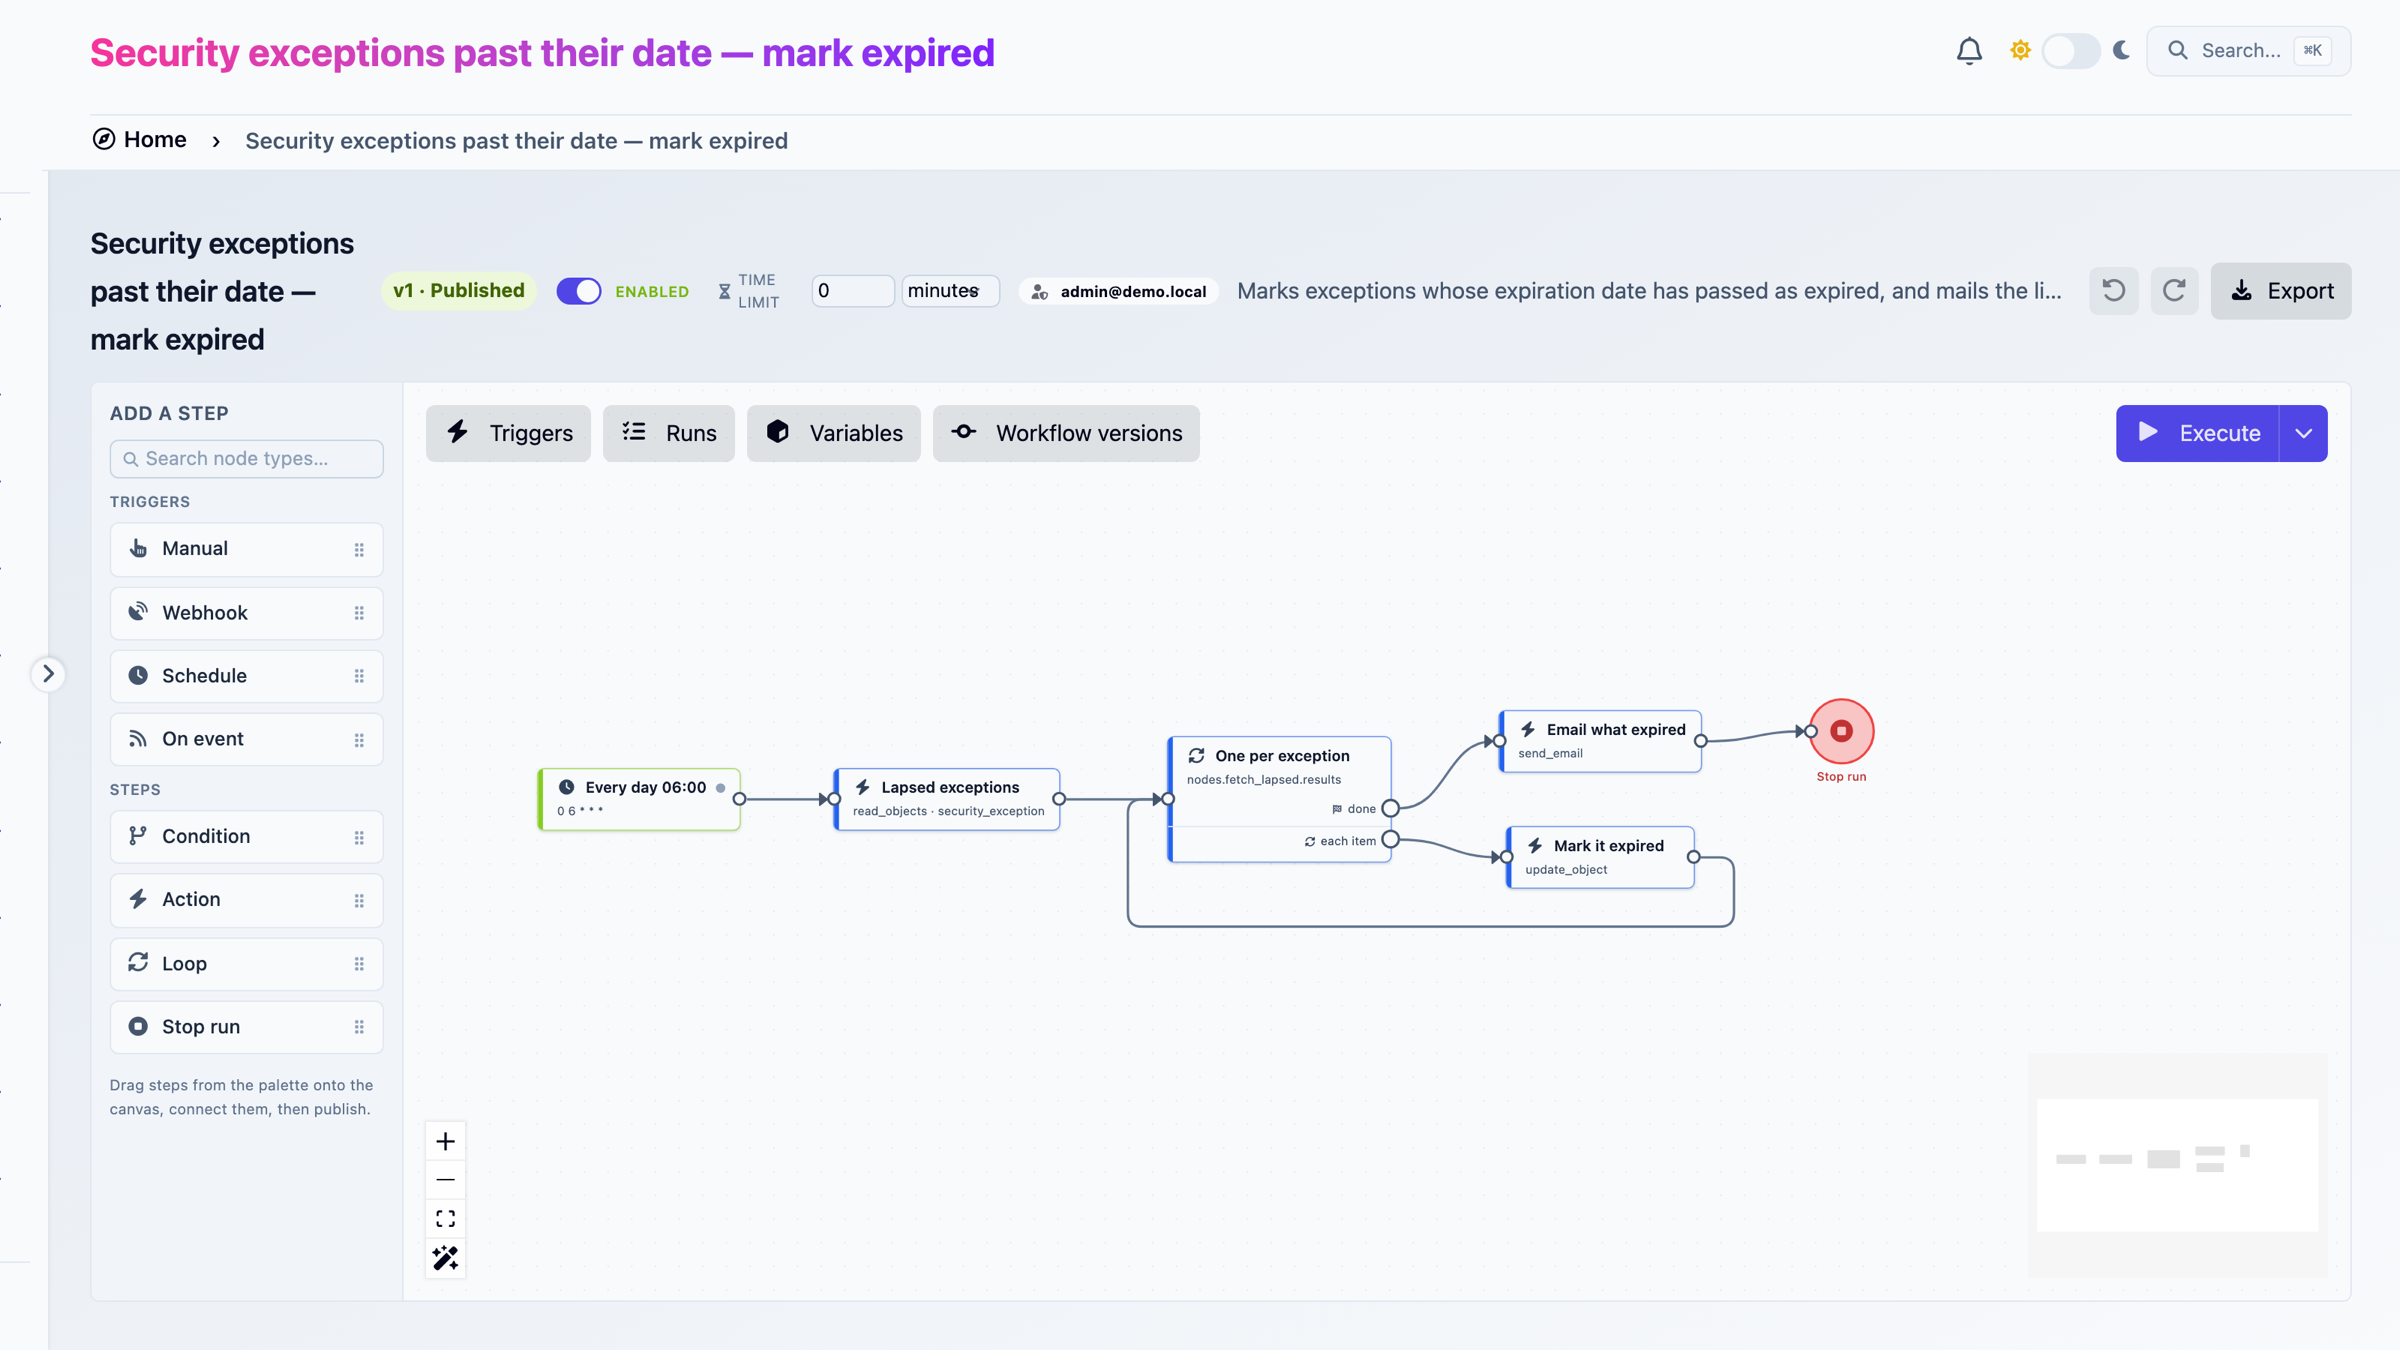
Automate the routine work
A visual builder with schedules, webhooks and events as triggers, then conditions, loops and actions on any object. Here, a daily run marks lapsed security exceptions as expired and emails the list.
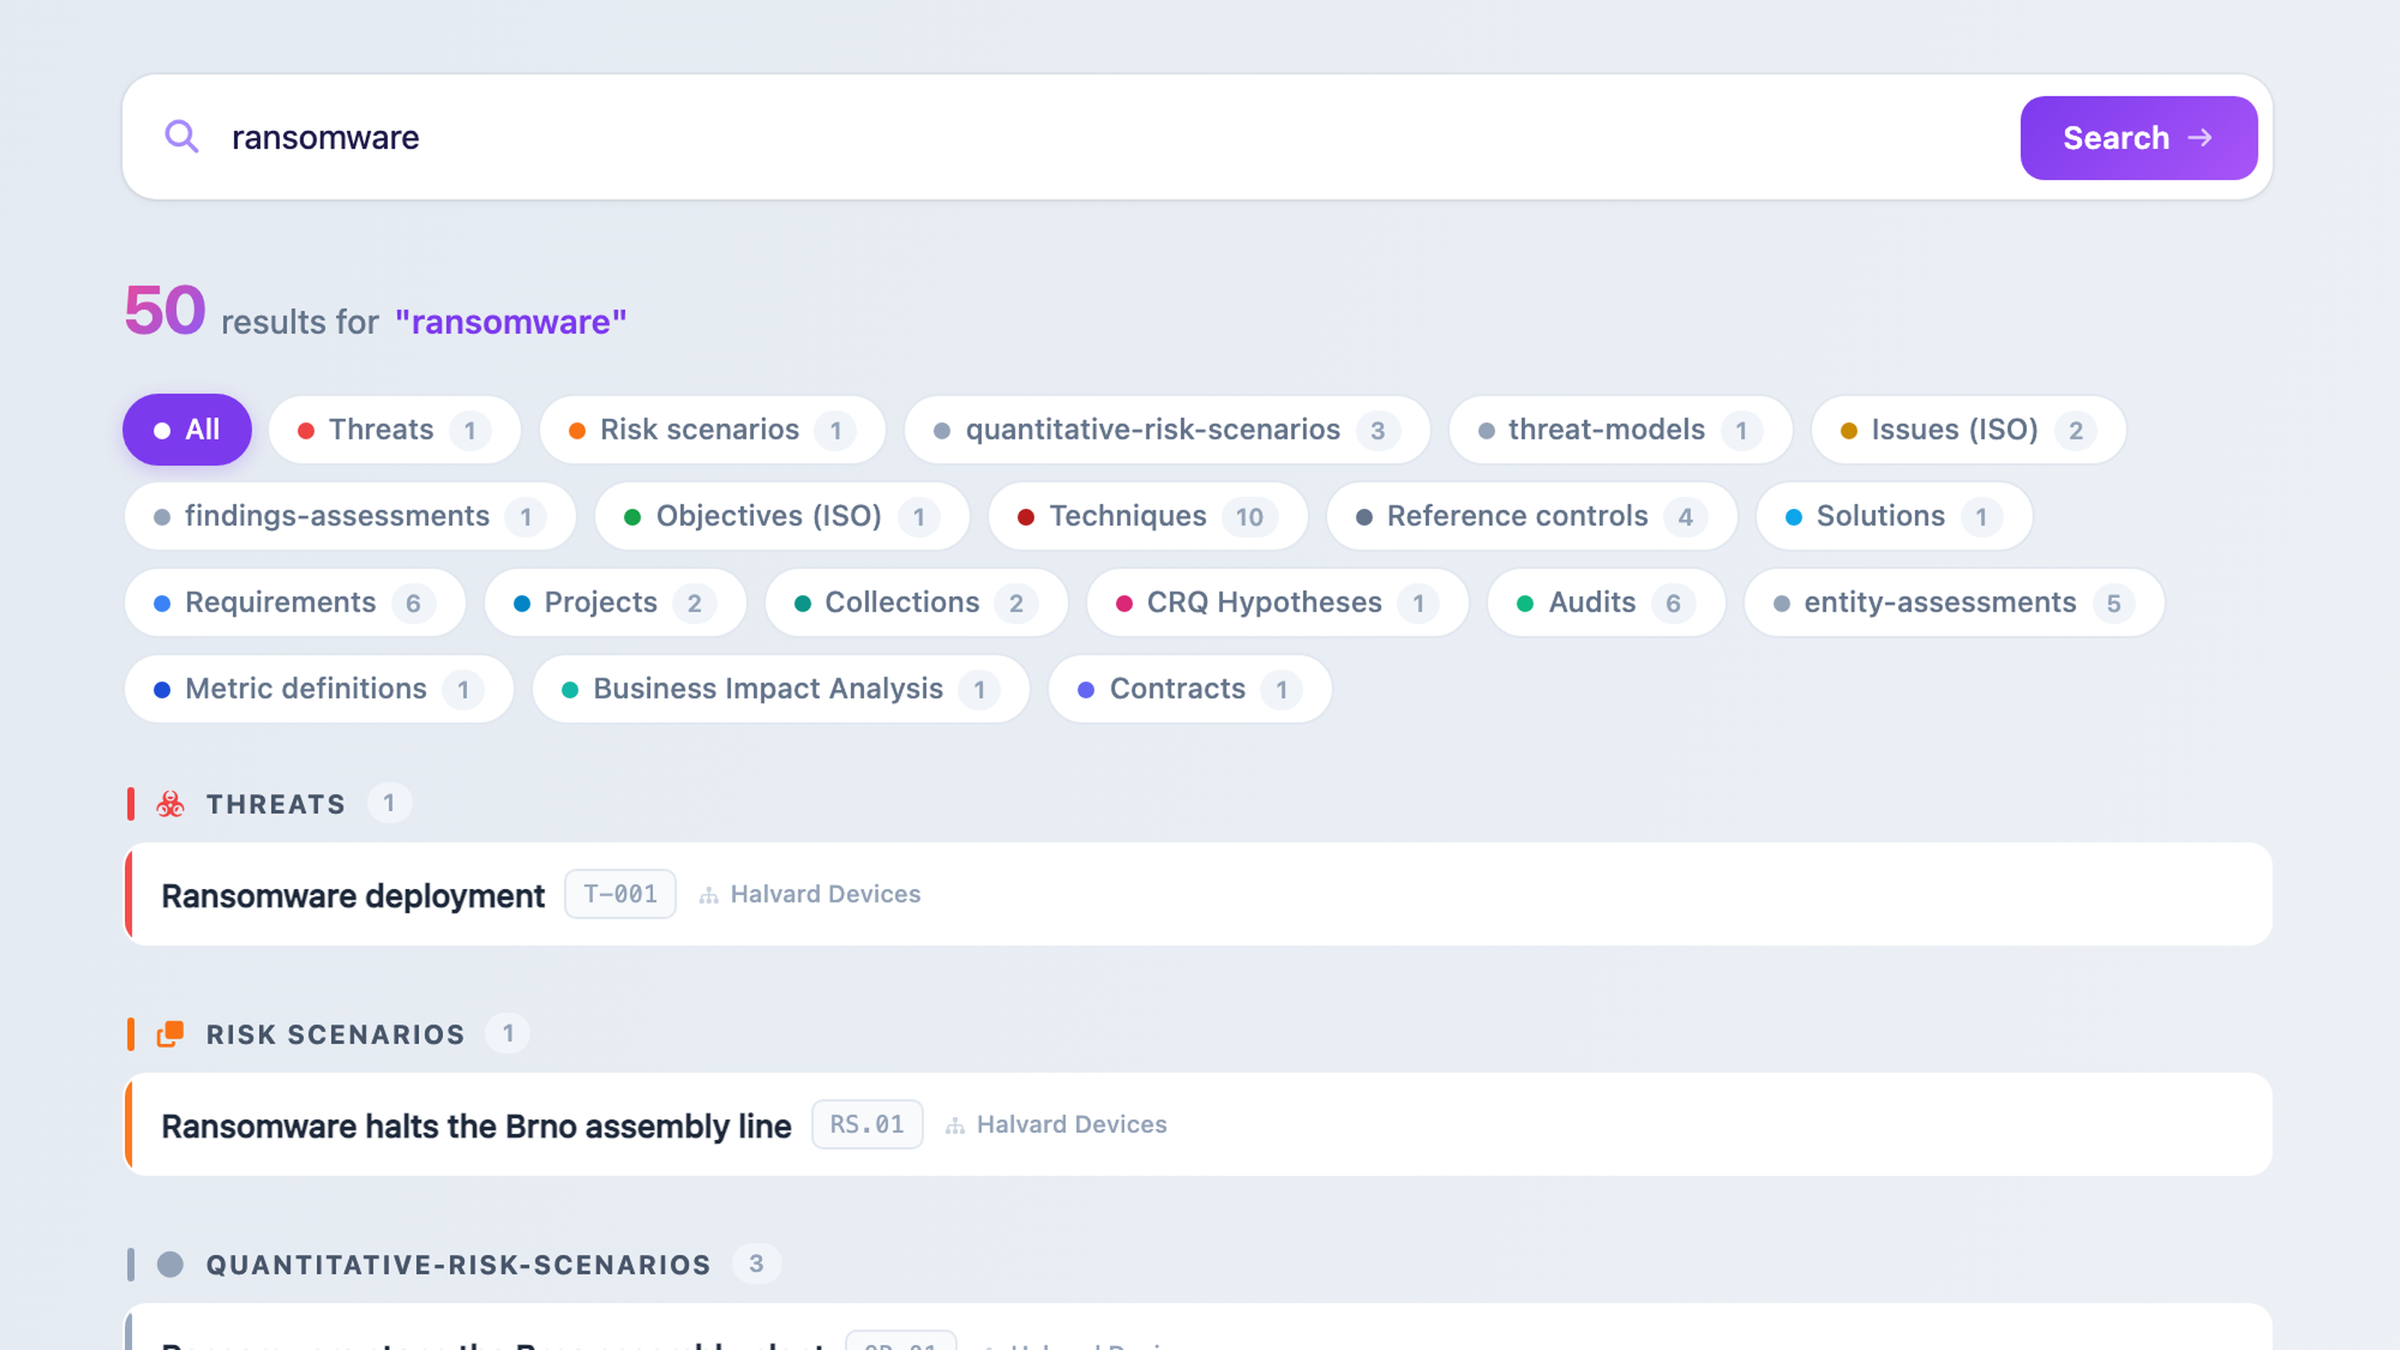
Search
Find anything, from anywhere
One search across every object: threats, scenarios, controls, audits, vendors, contracts and more, grouped by type. Press ⌘K from any page.
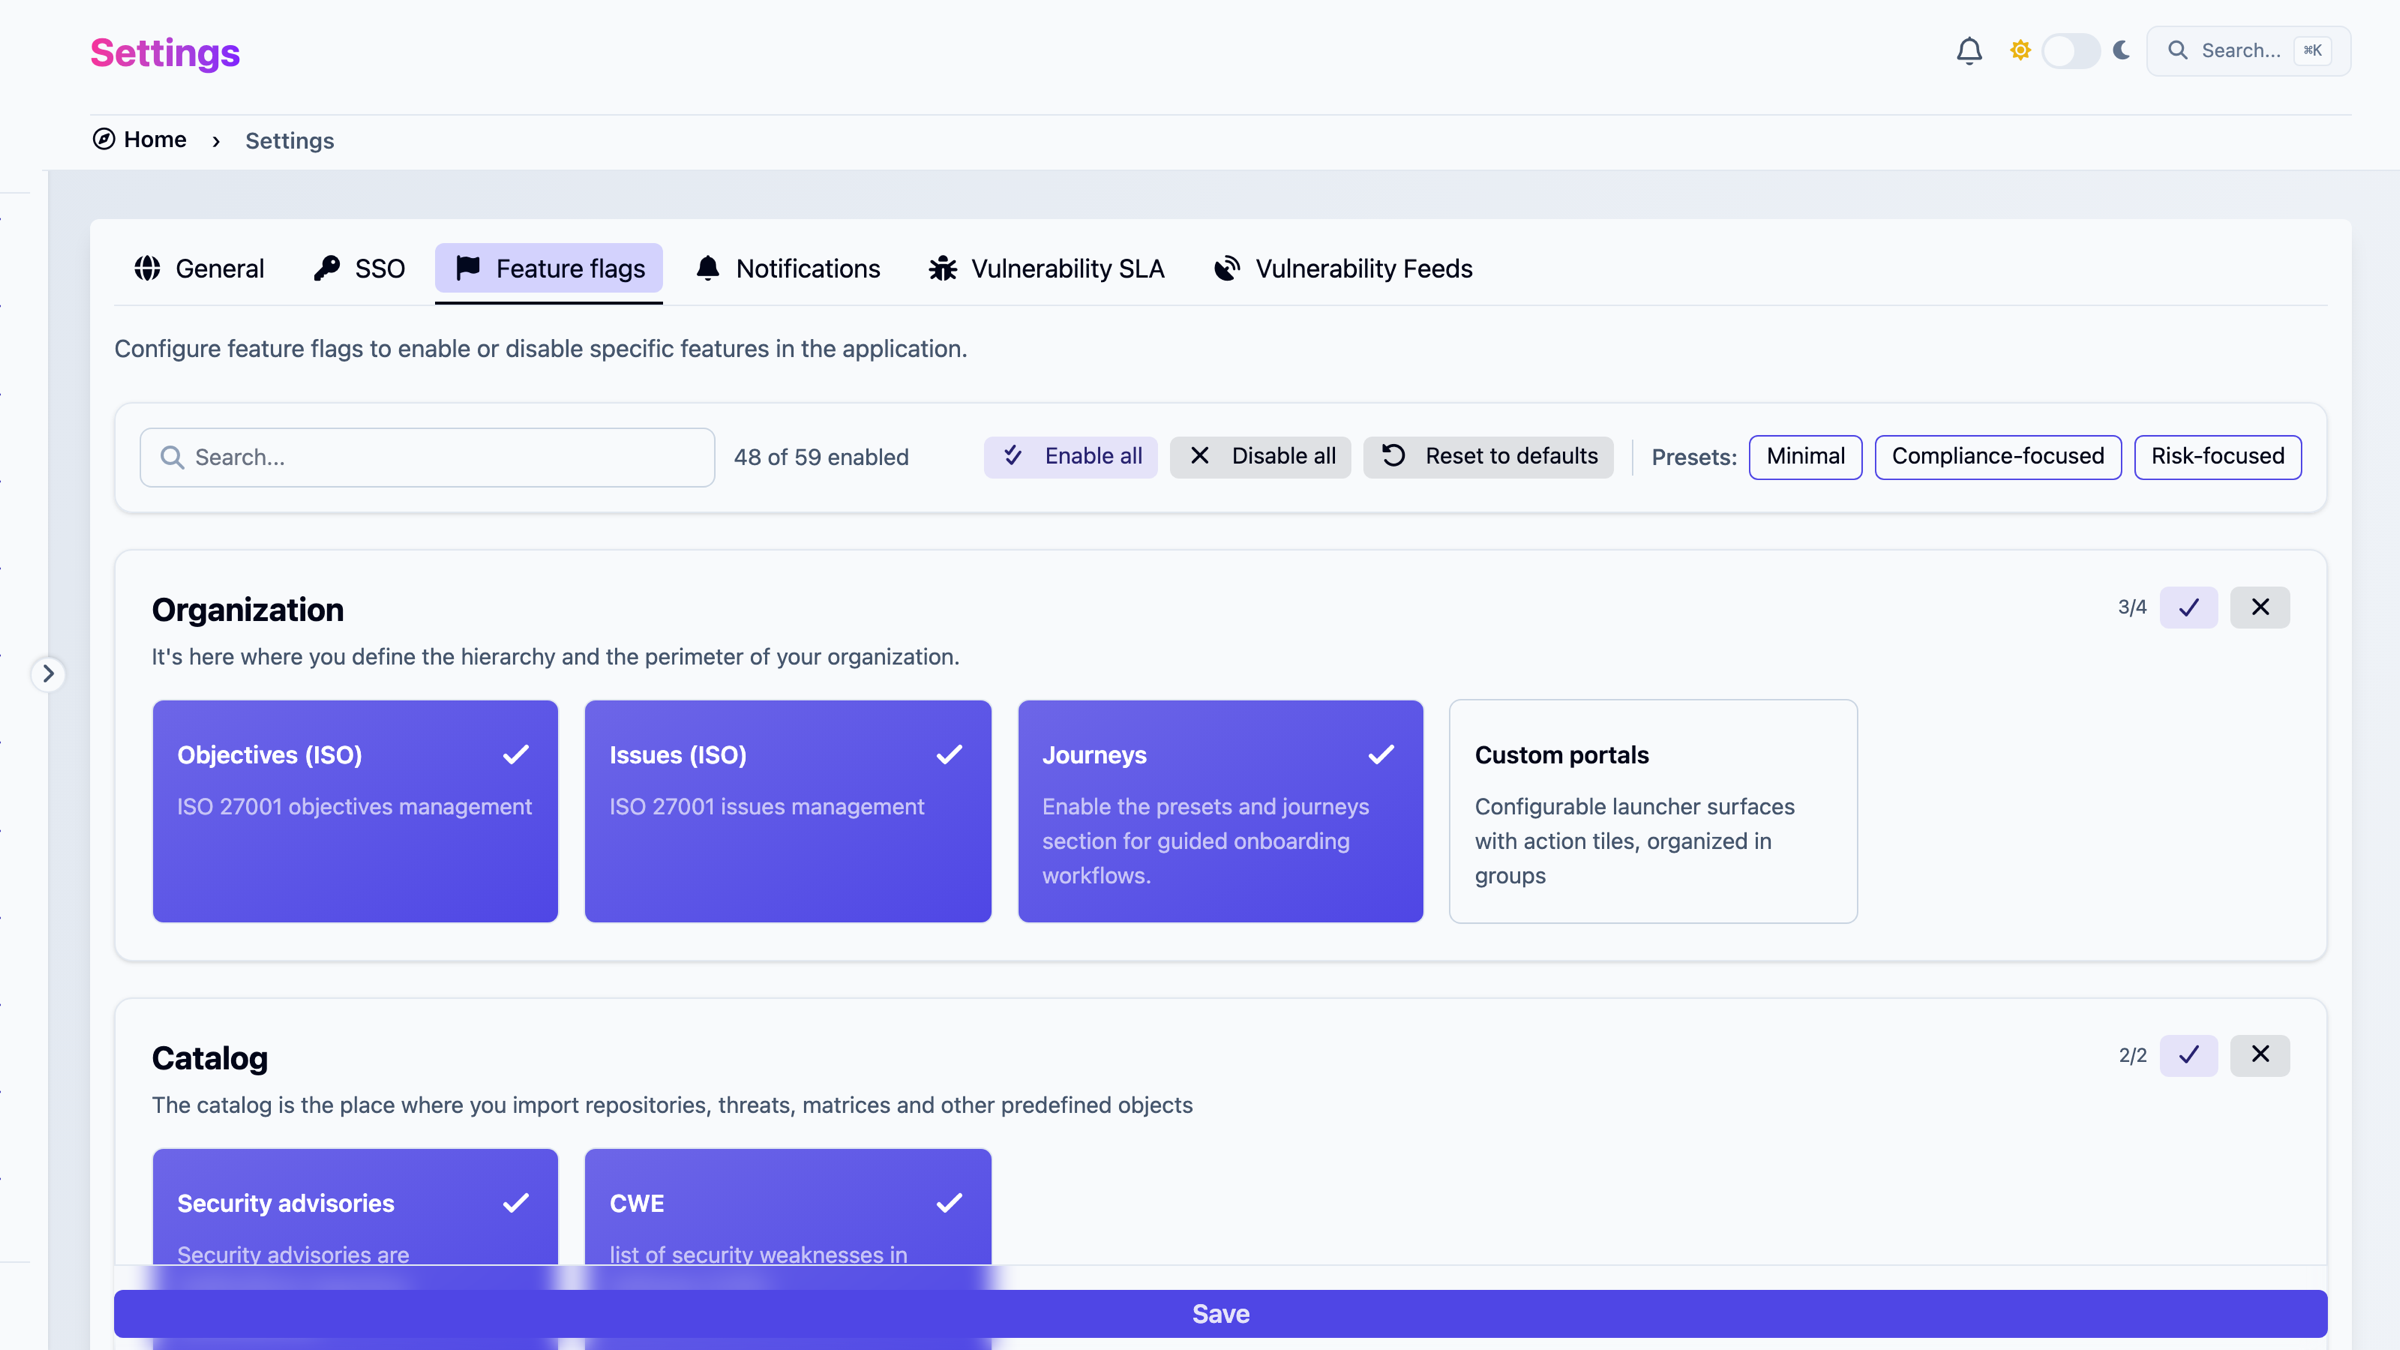
Feature flags
As light or as complete as you need
Turn modules on or off to fit the organisation: a small team can start with the essentials, a large one can open everything. Presets get you going in one click.
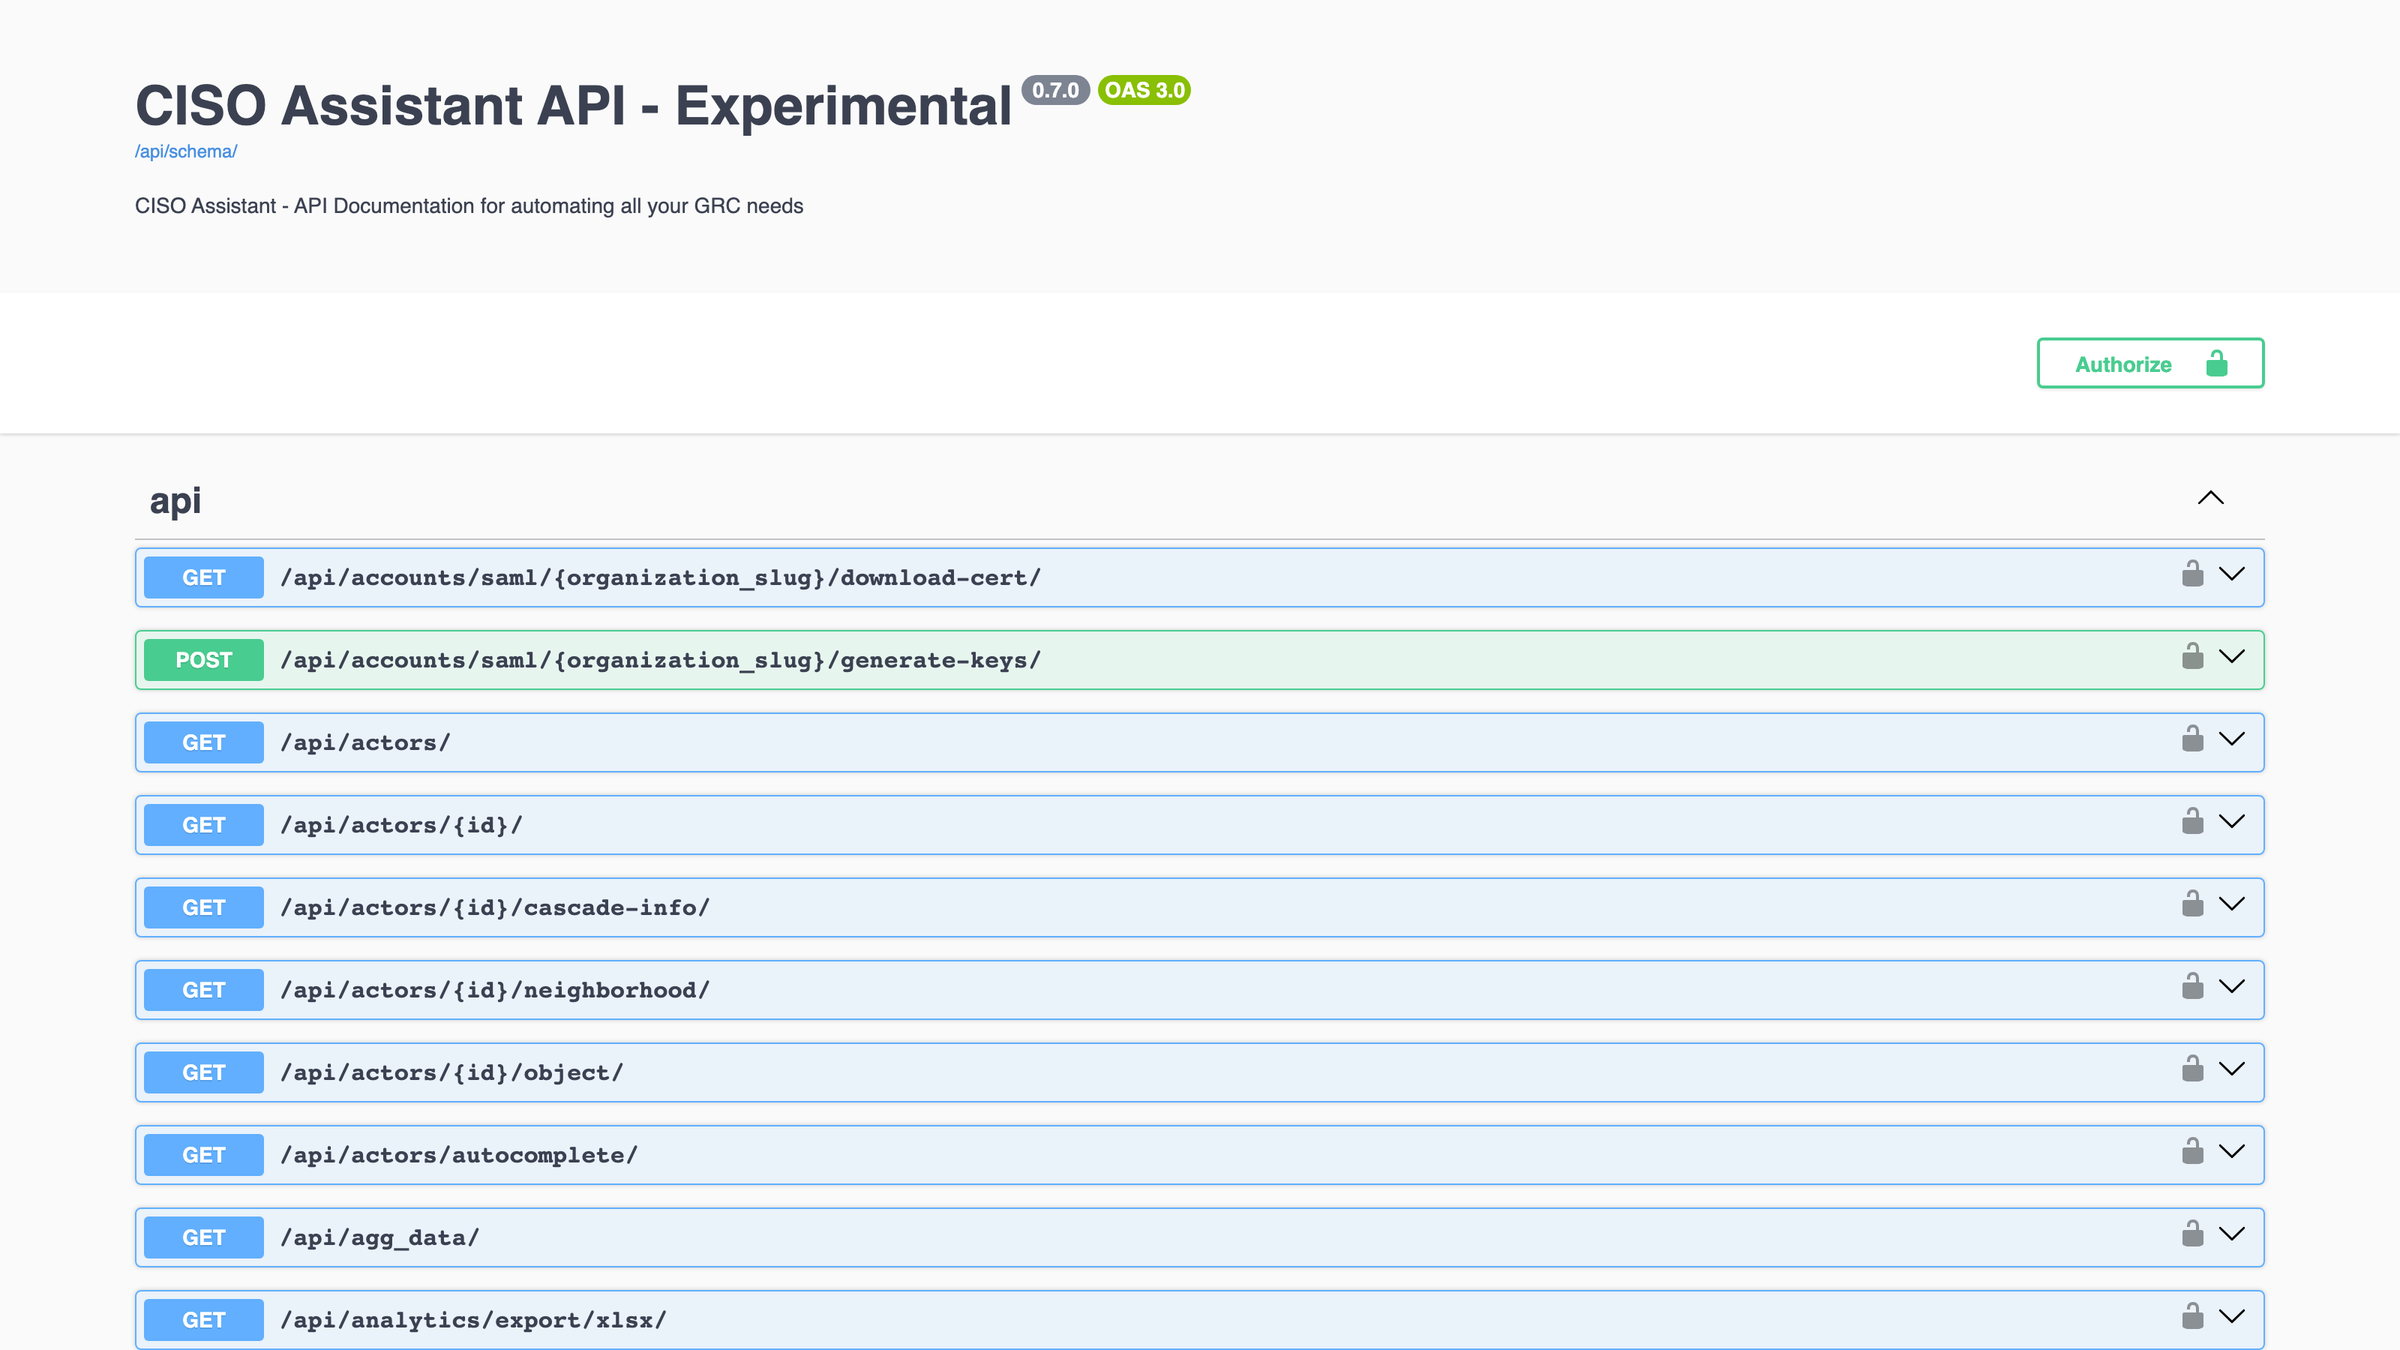
API
A REST API for everything you see
Automate imports, exports and reporting through the documented REST API, and connect your own tools.
Try it on your own data
Open a free trial instance and walk through these screens with your own frameworks, risks and controls.